Privacy Policy
Table of Contents
- Introduction and Overview
- Scope
- Legal Bases
- Contact Details of the Controller
- Storage Period
- Rights under the General Data Protection Regulation
- Data Transfer to Third Countries
- Security of Data Processing
- Communication
- Data Processing Agreement (DPA)
- Cookies
- Web Hosting Introduction
- Web Analytics Introduction
- Content Delivery Networks Introduction
- Cookie Consent Management Platform Introduction
- Security & Anti-Spam
- Web Design Introduction
- Online Map Services Introduction
- Content Search Providers Introduction
- Other Services Introduction
- Explanation of Terms Used
- Closing Remarks
Introduction and Overview
We have written this privacy policy (version 21.01.2026-113097992) in order to explain to you, in accordance with the requirements of the General Data Protection Regulation (EU) 2016/679 and applicable national laws, which personal data (data for short) we as the controller – and the processors commissioned by us (e.g. providers) – process, will process in the future and what legal options you have. The terms used are to be understood as gender-neutral.
In short: We inform you comprehensively about the data we process about you.
Privacy policies usually sound very technical and use legal jargon. This privacy policy, however, is intended to describe the most important things to you as simply and transparently as possible. Where it helps transparency, technical terms are explained in a reader-friendly way, links to further information are provided and graphics are used. In this way we inform you in clear and simple language that, in the course of our business activities, we only process personal data if there is a corresponding legal basis. This is certainly not possible with explanations that are as brief, unclear and legal-technical as possible, as is often standard on the internet when it comes to data protection. I hope you find the following explanations interesting and informative, and perhaps there is some information you did not yet know.
If questions remain nevertheless, we kindly ask you to contact the responsible body named below or in the legal notice (Impressum), to follow the links provided and to look at further information on third-party sites. Of course, you can also find our contact details in the legal notice (Impressum).
Scope
This privacy policy applies to all personal data processed by us in the company and to all personal data processed by companies commissioned by us (processors). By personal data we mean information within the meaning of Art. 4 No. 1 GDPR, such as a person's name, email address and postal address. The processing of personal data ensures that we can offer and invoice our services and products, whether online or offline. The scope of this privacy policy includes:
- all online presences (websites, online shops) that we operate
- social media presences and email communication
- mobile apps for smartphones and other devices
In short: This privacy policy applies to all areas in which personal data is processed in a structured manner in the company via the channels mentioned. Should we enter into legal relationships with you outside these channels, we will inform you separately if necessary.
Legal Bases
In the following privacy policy, we provide you with transparent information on the legal principles and regulations, i.e. the legal bases of the General Data Protection Regulation, which allow us to process personal data.
As far as EU law is concerned, we refer to REGULATION (EU) 2016/679 OF THE EUROPEAN PARLIAMENT AND OF THE COUNCIL of 27 April 2016. You can of course read this General Data Protection Regulation of the EU online on EUR-Lex, the gateway to EU law, at https://eur-lex.europa.eu/legal-content/DE/ALL/?uri=celex%3A32016R0679 .
We only process your data if at least one of the following conditions applies:
- Consent (Article 6(1)(a) GDPR): You have given us your consent to process data for a specific purpose. An example would be storing the data you entered in a contact form.
- Contract (Article 6(1)(b) GDPR): We process your data in order to fulfil a contract or pre-contractual obligations with you. For example, if we conclude a purchase contract with you, we need personal information in advance.
- Legal obligation (Article 6(1)(c) GDPR): If we are subject to a legal obligation, we process your data. For example, we are legally obliged to keep invoices for accounting purposes. These usually contain personal data.
- Legitimate interests (Article 6(1)(f) GDPR): In the case of legitimate interests that do not restrict your fundamental rights, we reserve the right to process personal data. For example, we have to process certain data in order to operate our website securely and economically efficiently. This processing is therefore a legitimate interest.
Other conditions, such as the performance of tasks in the public interest and the exercise of official authority, as well as the protection of vital interests, do not usually apply to us. Should such a legal basis be relevant after all, it will be indicated at the appropriate point.
In addition to the EU regulation, national laws also apply:
- In Austria this is the Federal Act on the Protection of Natural Persons with regard to the Processing of Personal Data (Data Protection Act), abbreviated DSG.
- In Germany the applicable law is the Federal Data Protection Act, abbreviated BDSG.
If other regional or national laws apply, we will inform you about them in the following sections.
Contact Details of the Controller
If you have any questions about data protection or the processing of personal data, you will find the contact details of the controller in accordance with Article 4(7) of the EU General Data Protection Regulation (GDPR) below:
Gökhan Simsek
Ernst-Jandl-Weg 6/7,
1220 Vienna,
Austria
Email: info@ninety-nine.at
Phone: +43 660 272 80 27
Legal notice (Impressum): https://www.ninety-nine.at/impressum.html
Storage Period
Our general criterion is that we only store personal data for as long as is absolutely necessary to provide our services and products. This means that we delete personal data as soon as the reason for the data processing no longer exists. In some cases we are legally obliged to store certain data even after the original purpose has ceased to apply, for example for accounting purposes.
Should you wish your data to be deleted or revoke your consent to data processing, the data will be deleted as quickly as possible, provided there is no obligation to store it.
We will inform you about the specific duration of the respective data processing below, provided we have further information on this.
Rights under the General Data Protection Regulation
In accordance with Articles 13 and 14 GDPR, we inform you of the following rights to which you are entitled, so that data is processed fairly and transparently:
- According to Article 15 GDPR, you have a right of access to information as to whether we process your data. If this is the case, you have the right to receive a copy of the data and to be told the following information:
- the purpose for which we carry out the processing;
- the categories, i.e. the types of data that are processed;
- who receives this data and, if the data is transferred to third countries, how its security can be guaranteed;
- how long the data will be stored;
- the existence of the right to rectification, erasure or restriction of processing and the right to object to the processing;
- that you can lodge a complaint with a supervisory authority (links to these authorities can be found below);
- the origin of the data if we did not collect it from you;
- whether profiling is carried out, i.e. whether data is automatically evaluated in order to create a personal profile of you.
- According to Article 16 GDPR, you have the right to rectification of the data, which means that we must correct data if you find errors.
- According to Article 17 GDPR, you have the right to erasure (“right to be forgotten”), which specifically means that you may request the deletion of your data.
- According to Article 18 GDPR, you have the right to restriction of processing, which means that we may only store the data but not use it further.
- According to Article 20 GDPR, you have the right to data portability, which means that we will provide you with your data in a common format on request.
- According to Article 21 GDPR, you have a right to object, which, once enforced, results in a change in processing.
- If the processing of your data is based on Article 6(1)(e) (public interest, exercise of official authority) or Article 6(1)(f) (legitimate interest), you can object to the processing. We will then check as quickly as possible whether we can legally comply with this objection.
- If data is used for direct advertising, you can object to this type of data processing at any time. We may then no longer use your data for direct marketing.
- If data is used for profiling, you can object to this type of data processing at any time. We may then no longer use your data for profiling.
- According to Article 22 GDPR, you may have the right not to be subject to a decision based solely on automated processing (for example profiling).
- According to Article 77 GDPR, you have the right to lodge a complaint. This means that you can complain to the data protection authority at any time if you believe that the processing of personal data violates the GDPR.
In short: You have rights – do not hesitate to contact the responsible body listed above!
If you believe that the processing of your data violates data protection law or that your data protection rights have been infringed in any other way, you can lodge a complaint with the supervisory authority. For Austria, this is the Data Protection Authority (Datenschutzbehörde), whose website you can find at https://www.dsb.gv.at/ . In Germany, there is a data protection commissioner for each federal state. For more information, you can contact the Federal Commissioner for Data Protection and Freedom of Information (BfDI) . The following local data protection authority is responsible for our company:
Austria Data Protection Authority (Datenschutzbehörde)
Head: Dr. Matthias Schmidl
Address: Barichgasse 40-42, 1030 Wien
Phone: +43 1 52 152-0
Email address:
dsb@dsb.gv.at
Website:
https://www.dsb.gv.at/
Data Transfer to Third Countries
We only transfer or process data in countries outside the scope of the GDPR (third countries) if you consent to this processing or if there is another legal permission. This applies in particular if the processing is required by law or necessary for the performance of a contractual relationship, and in any case only to the extent that this is generally permitted. In most cases, your consent is the most important reason for us to have data processed in third countries. The processing of personal data in third countries such as the USA, where many software manufacturers offer services and have their server locations, can mean that personal data is processed and stored in unexpected ways.
We expressly point out that, according to the European Court of Justice, there is currently only an adequate level of protection for data transfers to the USA if a US company that processes personal data of EU citizens in the USA is an active participant in the EU-US Data Privacy Framework. You can find more information on this at: https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en
Data processing by US services that are not active participants in the EU-US Data Privacy Framework may result in data being processed and stored without anonymisation. Furthermore, US government authorities may be able to access individual data. It may also happen that collected data is linked with data from other services of the same provider if you have a corresponding user account. Where possible, we try to use server locations within the EU, if this is offered.
We will inform you in more detail about data transfers to third countries at the appropriate points in this privacy policy, if applicable.
Security of Data Processing
To protect personal data, we have implemented both technical and organisational measures. Where possible, we encrypt or pseudonymise personal data. In this way, within our means, we make it as difficult as possible for third parties to infer personal information from our data.
Art. 25 GDPR speaks here of “data protection by design and by default”, meaning that security should always be considered for both software (e.g. forms) and hardware (e.g. access to the server room) and appropriate measures taken. Below we go into specific measures where necessary.
TLS encryption with https
TLS, encryption and https sound very technical, and they are. We use HTTPS (Hypertext Transfer Protocol Secure) to transmit data securely over the internet so that it cannot be intercepted.
This means that the complete transmission of all data from your browser to our web server is secured – nobody can “listen in”.
In this way we have introduced an additional layer of security and comply with data protection by design (Article 25(1) GDPR). By using TLS (Transport Layer Security), an encryption protocol for secure data transmission on the internet, we can ensure the protection of confidential data.
You can recognise the use of this protection of data transmission by the small lock symbol  at the top left of the browser, to the left of the internet address (e.g. examplepage.com), and by the use of the https scheme (instead of http) as part of our internet address.
If you want to know more about encryption, we recommend a Google search for “Hypertext Transfer Protocol Secure wiki” to find good links to further information.
Communication
|
Communication Summary
👥 Data subjects: everyone who communicates with us by phone, email or online form 📓 Data processed: e.g. phone number, name, email address, form data entered. You can find more details on this under the respective type of contact used 🤝 Purpose: handling communication with customers, business partners, etc. 📅 Storage period: duration of the business case and the statutory provisions ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(b) GDPR (contract), Art. 6(1)(f) GDPR (legitimate interests) |
If you contact us and communicate by phone, email or online form, personal data may be processed.
The data is processed to handle and process your question and the related business transaction. The data is stored for exactly that long or for as long as the law requires.
Data subjects
The processes described affect everyone who contacts us via the communication channels we provide.
Phone
When you call us, the call data is stored in pseudonymised form on the respective device and with the telecommunications provider used. In addition, data such as name and phone number may subsequently be sent by email and stored in order to answer the enquiry. The data is deleted as soon as the business case has been concluded and legal requirements permit.
When you communicate with us by email, data may be stored on the respective device (computer, laptop, smartphone,…) and data is stored on the email server. The data is deleted as soon as the business case has been concluded and legal requirements permit.
Online forms
When you communicate with us using an online form, data is stored on our web server and, where applicable, forwarded to one of our email addresses. The data is deleted as soon as the business case has been concluded and legal requirements permit.
Legal Bases
The processing of the data is based on the following legal bases:
- Art. 6(1)(a) GDPR (consent): You give us your consent to store your data and to continue to use it for purposes relating to the business case;
- Art. 6(1)(b) GDPR (contract): It is necessary for the performance of a contract with you or a processor such as the telephone provider, or we need to process the data for pre-contractual activities, such as preparing an offer;
- Art. 6(1)(f) GDPR (legitimate interests): We want to handle customer enquiries and business communication in a professional manner. For this, certain technical facilities such as email programs, Exchange servers and mobile network operators are necessary in order to operate communication efficiently.
Data Processing Agreement (DPA)
In this section we would like to explain to you what a data processing agreement is and why it is needed. Because the term “data processing agreement” is quite a mouthful, we will often use only the acronym DPA in this text. Like most companies, we do not work alone but also use the services of other companies or individuals ourselves. By involving various companies or service providers, we may pass on personal data for processing. These partners then act as processors, with whom we conclude a contract, the so-called data processing agreement (DPA). The most important thing for you to know is that your personal data is processed exclusively according to our instructions and must be regulated by the DPA.
Who are processors?
As a company and website owner, we are responsible for all data that we process from you. In addition to the controllers, there may also be so-called processors. This includes any company or person that processes personal data on our behalf. More precisely, and according to the GDPR definition: any natural or legal person, public authority, agency or other body that processes personal data on our behalf is considered a processor. Processors can therefore be service providers such as hosting or cloud providers, payment or newsletter providers, or large companies such as Google or Microsoft.
For a better understanding of the terms, here is an overview of the three roles in the GDPR:
Data subject (you as a customer or prospect) → Controller (we as the company and client) → Processor (service providers such as web hosts or cloud providers)
Content of a data processing agreement
As already mentioned above, we have concluded a DPA with our partners who act as processors. Above all, it states that the processor processes the data exclusively in accordance with the GDPR. The contract must be concluded in writing, although in this context an electronic conclusion of contract also counts as “in writing”. The personal data is only processed on the basis of the contract. The contract must contain the following:
- commitment to us as the controller
- obligations and rights of the controller
- categories of data subjects
- type of personal data
- nature and purpose of the data processing
- subject matter and duration of the data processing
- location where the data processing is carried out
Furthermore, the contract contains all obligations of the processor. The most important obligations are:
- to ensure data security measures
- to take possible technical and organisational measures to protect the rights of the data subject
- to keep a record of processing activities
- to cooperate with the data protection supervisory authority on request
- to carry out a risk analysis with regard to the personal data received
- sub-processors may only be engaged with the written approval of the controller
You can see what such a DPA looks like in practice, for example, at https://www.wko.at/service/wirtschaftsrecht-gewerberecht/eu-dsgvo-mustervertrag-auftragsverarbeitung.html . A model contract is presented there.
Cookies
|
Cookies Summary
👥 Data subjects: visitors to the website 🤝 Purpose: depends on the respective cookie. You can find more details below or from the manufacturer of the software that sets the cookie. 📓 Data processed: depends on the cookie used. You can find more details below or from the manufacturer of the software that sets the cookie. 📅 Storage period: depends on the respective cookie, can vary from hours to years ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What are cookies?
Our website uses HTTP cookies to store user-specific data.
Below we explain what cookies are and why they are used, so that you can better understand the following privacy policy.
Whenever you surf the internet, you use a browser. Well-known browsers include Chrome, Safari, Firefox, Internet Explorer and Microsoft Edge. Most websites store small text files in your browser. These files are called cookies.
One thing cannot be denied: cookies are really useful little helpers. Almost all websites use cookies. More precisely, they are HTTP cookies, as there are also other cookies for other areas of application. HTTP cookies are small files that are stored on your computer by our website. These cookie files are automatically placed in the cookie folder, effectively the “brain” of your browser. A cookie consists of a name and a value. When defining a cookie, one or more attributes must also be specified.
Cookies store certain user data about you, such as language or personal page settings. When you visit our site again, your browser transmits the “user-related” information back to our site. Thanks to cookies, our website knows who you are and offers you the settings you are used to. In some browsers each cookie has its own file, in others, such as Firefox, all cookies are stored in a single file.
The following graphic shows a possible interaction between a web browser such as Chrome and the web server. The web browser requests a website and receives a cookie back from the server, which the browser uses again as soon as another page is requested.
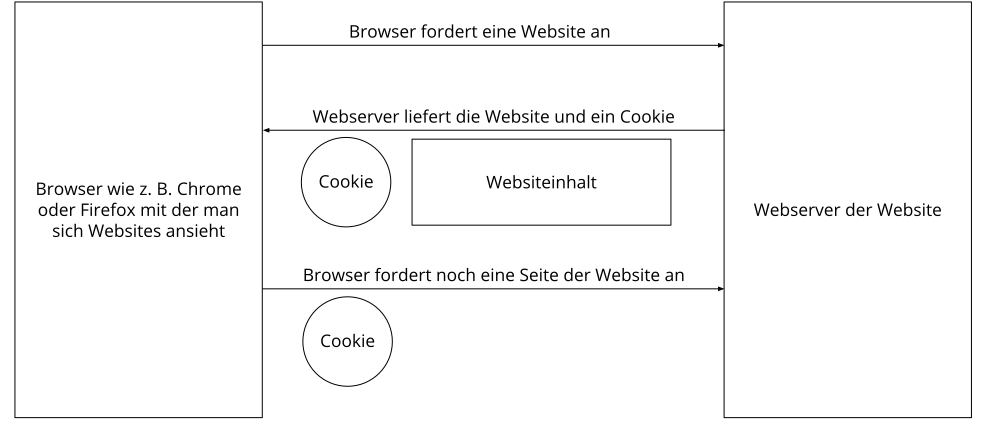
There are both first-party cookies and third-party cookies. First-party cookies are created directly by our site, third-party cookies are created by partner websites (e.g. Google Analytics). Each cookie must be assessed individually, as each cookie stores different data. The expiry time of a cookie also varies from a few minutes to a few years. Cookies are not software programs and do not contain viruses, trojans or other “pests”. Cookies also cannot access information on your PC.
This is an example of what cookie data can look like:
Name: _ga
Value: GA1.2.1326744211.152113097992-9
Purpose: Distinguishing website visitors
Expiry date: after 2 years
A browser should be able to support these minimum sizes:
- At least 4096 bytes per cookie
- At least 50 cookies per domain
- At least 3000 cookies in total
What types of cookies are there?
The question of which cookies we use in particular depends on the services used and is clarified in the following sections of the privacy policy. At this point we would like to briefly discuss the different types of HTTP cookies.
There are 4 types of cookies:
Essential cookies
These cookies are necessary to ensure basic functions of the website. For example, these cookies are needed when a user puts a product in the shopping cart, then continues browsing other pages and only goes to the checkout later. These cookies ensure that the shopping cart is not deleted, even if the user closes the browser window.
Functional cookies
These cookies collect information about user behaviour and whether the user receives any error messages. In addition, these cookies are used to measure the loading time and the behaviour of the website in different browsers.
Target-oriented cookies
These cookies ensure better user-friendliness. For example, entered locations, font sizes or form data are stored.
Advertising cookies
These cookies are also called targeting cookies. They serve to deliver individually tailored advertising to the user. This can be very practical, but also very annoying.
Usually, when you visit a website for the first time, you are asked which of these types of cookies you want to allow. And of course this decision is also stored in a cookie.
If you want to know more about cookies and are not afraid of technical documentation, we recommend https://datatracker.ietf.org/doc/html/rfc6265, the Request for Comments of the Internet Engineering Task Force (IETF) called “HTTP State Management Mechanism”.
Purpose of processing via cookies
Ultimately, the purpose depends on the respective cookie. You can find more details below or from the manufacturer of the software that sets the cookie.
What data is processed?
Cookies are little helpers for many different tasks. Unfortunately, it is not possible to generalise which data is stored in cookies, but we will inform you about the data processed or stored in the following privacy policy.
Storage period of cookies
The storage period depends on the respective cookie and is specified further below. Some cookies are deleted after less than an hour, others can remain stored on a computer for several years.
You also have influence over the storage period yourself. You can manually delete all cookies at any time via your browser (see also “Right to object” below). Furthermore, cookies based on consent are deleted at the latest after you withdraw your consent, whereby the lawfulness of storage up to that point remains unaffected.
Right to object – how can I delete cookies?
You decide yourself how and whether you want to use cookies. Regardless of which service or website the cookies come from, you always have the option of deleting cookies, deactivating them or only partially allowing them. For example, you can block third-party cookies but allow all other cookies.
If you want to find out which cookies have been stored in your browser, or if you want to change or delete cookie settings, you can find this in your browser settings:
Chrome: Delete, allow and manage cookies in Chrome
Safari: Manage cookies and website data in Safari
Firefox: Clear cookies to remove data that websites have stored on your computer
Internet Explorer: Delete and manage cookies
Microsoft Edge: Delete and manage cookies
If you generally do not want cookies, you can set up your browser so that it always informs you when a cookie is to be set. This way you can decide for each individual cookie whether to allow it or not. The procedure varies depending on the browser. It is best to search for the instructions on Google using the search term “delete cookies Chrome” or “disable cookies Chrome” in the case of a Chrome browser.
Legal basis
The so-called “Cookie Directive” has existed since 2009. It states that the storage of cookies requires your Consent (Article 6(1)(a) GDPR). Within the EU countries, however, there are still very different reactions to this directive. In Austria, this directive was implemented in Section 165(3) of the Telecommunications Act (2021). In Germany, the Cookie Directive was not implemented as national law. Instead, this directive was largely implemented in Section 15(3) of the Telemedia Act (TMG), which was replaced by the Digital Services Act (DDG) in May 2024.
For strictly necessary cookies, even where no consent has been given, there are legitimate interests (Article 6(1)(f) GDPR), which in most cases are of an economic nature. We want to provide visitors to the website with a pleasant user experience, and certain cookies are often strictly necessary for this.
Insofar as cookies that are not strictly necessary are used, this only happens with your consent. The legal basis in this respect is Art. 6(1)(a) GDPR.
In the following sections you will be informed in more detail about the use of cookies, provided the software used uses cookies.
Web Hosting Introduction
|
Web Hosting Summary
👥 Data subjects: visitors to the website 🤝 Purpose: professional hosting of the website and securing its operation 📓 Data processed: IP address, time of website visit, browser used and other data. You can find more details below or from the respective web hosting provider used. 📅 Storage period: depends on the respective provider, but usually 2 weeks ⚖️ Legal bases: Art. 6(1)(f) GDPR (legitimate interests) |
What is web hosting?
When you visit websites these days, certain information – including personal data – is automatically created and stored, including on this website. This data should be processed as sparingly as possible and only with justification. By website, by the way, we mean the entirety of all web pages on a domain, i.e. everything from the start page (homepage) to the very last subpage (like this one). By domain we mean, for example, example.de or sampleexample.com.
If you want to view a website on a computer, tablet or smartphone, you use a program called a web browser. You probably know some web browsers by name: Google Chrome, Microsoft Edge, Mozilla Firefox and Apple Safari. We call it browser or web browser for short.
To display the website, the browser must connect to another computer where the website's code is stored: the web server. Operating a web server is a complicated and time-consuming task, which is why it is usually carried out by professional providers. They offer web hosting and thus ensure reliable and error-free storage of website data. A whole lot of technical terms, but please stay with us, it gets even better!
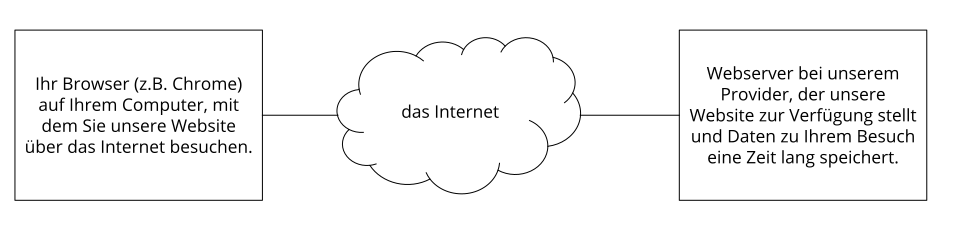
When the browser on your computer (desktop, laptop, tablet or smartphone) connects and during data transmission to and from the web server, personal data may be processed. On the one hand, your computer stores data; on the other hand, the web server must also store data for a while to ensure proper operation.
A picture is worth a thousand words, so the following graphic illustrates the interaction between the browser, the internet and the hosting provider.
Why do we process personal data?
The purposes of data processing are:
- Professional hosting of the website and securing its operation
- to maintain operational and IT security
- Anonymous evaluation of access behaviour to improve our offer and, if necessary, for criminal prosecution or the pursuit of claims
What data is processed?
Even while you are visiting our website right now, our web server, which is the computer on which this website is stored, usually automatically stores data such as
- the complete internet address (URL) of the web page accessed
- browser and browser version (e.g. Chrome 87)
- the operating system used (e.g. Windows 10)
- the address (URL) of the previously visited page (referrer URL) (e.g. https://www.beispielquellsite.de/vondabinichgekommen/)
- the host name and IP address of the device from which access is made (e.g. COMPUTERNAME and 194.23.43.121)
- date and time
- in files, the so-called web server log files
How long is data stored?
As a rule, the data mentioned above is stored for two weeks and then automatically deleted. We do not pass on this data, but we cannot rule out that this data may be viewed by authorities in the event of unlawful conduct.
In short: Your visit is logged by our provider (the company that runs our website on special computers (servers)), but we do not pass on your data without consent!
Legal basis
The lawfulness of processing personal data in the context of web hosting results from Art. 6(1)(f) GDPR (safeguarding legitimate interests), as the use of professional hosting with a provider is necessary in order to present the company on the internet securely and in a user-friendly manner and to be able to pursue attacks and claims arising from this if necessary.
As a rule, there is a contract on data processing between us and the hosting provider in accordance with Art. 28 et seq. GDPR, which ensures compliance with data protection and guarantees data security.
Web Hosting Provider External Privacy Policy
Below you will find the contact details of our external hosting provider, where, in addition to the information above, you can find out more about data processing:
VPS host name:
Company name: CKStudio e.U.
Address: Webgasse 43/3D, 1060 Wien
Contact: info@ckstudio.at
Actual hosting provider:
easyname GmbH Canettistraße 5/10, 1100 Wien, Österreich
Email address: office@easyname.com
Phone: 01 353 2222
You can find out more about data processing by this provider in the Privacy Policy.
Web Analytics Introduction
|
Web Analytics Privacy Policy Summary
👥 Data subjects: visitors to the website 🤝 Purpose: evaluation of visitor information to optimise the website. 📓 Data processed: access statistics containing data such as access locations, device data, access duration and time, navigation behaviour, click behaviour and IP addresses. You can find more details on this from the respective web analytics tool used. 📅 Storage period: depends on the web analytics tool used ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is web analytics?
On our website we use software to evaluate the behaviour of website visitors, called web analytics for short. Data is collected that the respective analytics tool provider (also called tracking tool) stores, manages and processes. The data is used to create analyses of user behaviour on our website, which are made available to us as the website operator. In addition, most tools offer various testing options. For example, we can test which offers or content are best received by our visitors. To do this, we show you two different offers for a limited period. After the test (so-called A/B test), we know which product or content our website visitors find more interesting. For such testing procedures, as well as for other analytics procedures, user profiles can also be created and the data stored in cookies.
Why do we use web analytics?
We have a clear goal in mind with our website: we want to deliver the best web offering on the market for our industry. To achieve this goal, we want on the one hand to offer the best and most interesting offer, and on the other hand to make sure that you feel completely comfortable on our website. With the help of web analysis tools, we can take a closer look at the behaviour of our website visitors and then improve our web offering accordingly for you and for us. For example, we can see how old our visitors are on average, where they come from, when our website is visited most or which content or products are particularly popular. All this information helps us to optimise the website and thus adapt it as well as possible to your needs, interests and wishes.
What data is processed?
Exactly which data is stored naturally depends on the analysis tools used. As a rule, however, it is stored, for example, which content you view on our website, which buttons or links you click, when you call up a page, which browser you use, which device (PC, tablet, smartphone, etc.) you use to visit the website or which computer system you use. If you have agreed that location data may also be collected, this may also be processed by the web analysis tool provider.
Your IP address is also stored. According to the General Data Protection Regulation (GDPR), IP addresses are personal data. However, your IP address is usually stored in pseudonymised form (i.e. in an unrecognisable and shortened form). For the purpose of testing, web analysis and web optimisation, no direct data such as your name, age, address or email address is generally stored. All this data, if collected, is stored in pseudonymised form. This means that you cannot be identified as a person.
The following example schematically shows how Google Analytics works as an example of client-based web tracking with JavaScript code.
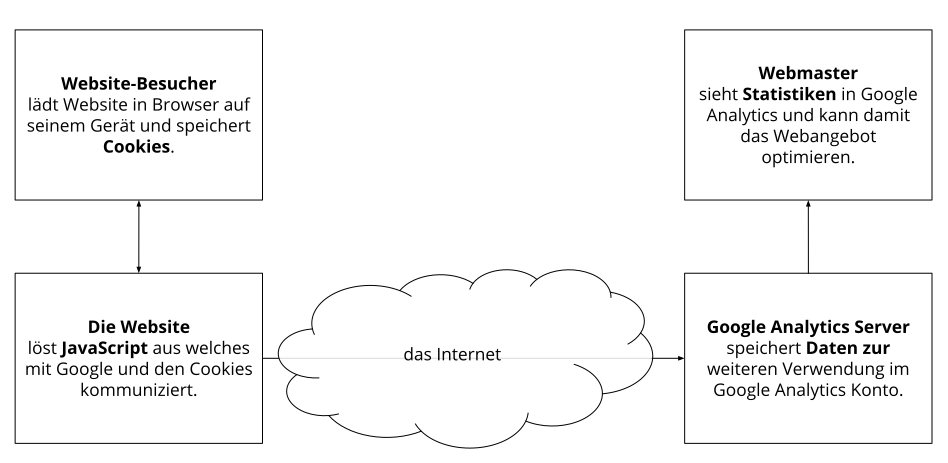
How long the respective data is stored always depends on the provider. Some cookies only store data for a few minutes or until you leave the website again, other cookies can store data for several years.
Duration of data processing
We will inform you about the duration of data processing below, provided we have further information on this. In general, we only process personal data for as long as is absolutely necessary to provide our services and products. If it is required by law, as in the case of accounting, for example, this storage period may also be exceeded.
Right to object
You also have the right and the possibility to withdraw your consent to the use of cookies or third-party providers at any time. This works either via our cookie management tool or via other opt-out functions. For example, you can also prevent data collection by cookies by managing, deactivating or deleting cookies in your browser.
Legal basis
The use of web analytics requires your consent, which we have obtained with our cookie pop-up. According to Art. 6(1)(a) GDPR (consent) , this consent constitutes the legal basis for the processing of personal data as may occur when it is collected by web analytics tools.
In addition to consent, we have a legitimate interest in analysing the behaviour of website visitors and thus improving our offer technically and economically. With the help of web analytics, we recognise website errors, can identify attacks and improve economic efficiency. The legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use the tools if you have given your consent.
Since cookies are used in web analytics tools, we also recommend that you read our general privacy policy on cookies. To find out exactly which data of yours is stored and processed, you should read the privacy policies of the respective tools.
Information on specific web analytics tools can be found – if available – in the following sections.
Google Analytics Privacy Policy
|
Google Analytics Privacy Policy Summary
👥 Data subjects: visitors to the website 🤝 Purpose: evaluation of visitor information to optimise the website. 📓 Data processed: access statistics containing data such as access locations, device data, access duration and time, navigation behaviour and click behaviour. You can find more details on this further down in this privacy policy. 📅 Storage period: individually adjustable, by default Google Analytics 4 stores data for 14 months ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is Google Analytics?
On our website we use the analytics tracking tool Google Analytics in the version Google Analytics 4 (GA4) of the American company Google Inc. For the European area, the company Google Ireland Limited (Gordon House, Barrow Street Dublin 4, Ireland) is responsible for all Google services. Google Analytics collects data about your actions on our website. However, through the combination of various technologies such as cookies, device IDs and login information, you as a user can be identified across different devices. As a result, your actions can also be analysed across platforms.
For example, if you click on a link, this event is stored in a cookie and sent to Google Analytics. With the help of the reports we receive from Google Analytics, we can better adapt our website and our service to your wishes. Below we go into more detail about the tracking tool and above all inform you about which data is processed and how you can prevent this.
Google Analytics is a tracking tool used to analyse the traffic on our website. These measurements and analyses are based on a pseudonymous user identification number. This number does not contain any personal data such as name or address, but serves to assign events to a device. GA4 uses an event-based model that captures detailed information about user interactions such as page views, clicks, scrolling and conversion events. In addition, various machine learning functions have been built into GA4 to better understand user behaviour and certain trends. With the help of machine learning functions, GA4 relies on modelling. This means that, on the basis of the data collected, missing data can also be extrapolated in order to optimise the analysis and also to be able to make forecasts.
In order for Google Analytics to work at all, a tracking code is built into the code of our website. When you visit our website, this code records various events that you perform on our website. With GA4's event-based data model, we as the website operator can define and track specific events in order to obtain analyses of user interactions. This means that, in addition to general information such as clicks or page views, special events that are important for our business can also be tracked. Such special events can be, for example, submitting a contact form or purchasing a product.
As soon as you leave our website, this data is sent to the Google Analytics servers and stored there.
Google processes the data and we receive reports about your user behaviour. These may include the following reports:
- Audience reports: Through audience reports we get to know our users better and know more precisely who is interested in our service.
- Advertising reports: Advertising reports make it easier for us to analyse and improve our online advertising.
- Acquisition reports: Acquisition reports give us helpful information on how we can get more people excited about our service.
- Behaviour reports: Here we learn how you interact with our website. We can track the path you take on our site and which links you click.
- Conversion reports: A conversion is a process in which you carry out a desired action as a result of a marketing message. For example, when you go from being a mere website visitor to a buyer or newsletter subscriber. With the help of these reports we learn more about how our marketing measures are received by you. In this way we want to increase our conversion rate.
- Real-time reports: Here we always find out immediately what is happening on our website right now. For example, we can see how many users are reading this text right now.
In addition to the analysis reports mentioned above, Google Analytics 4 also offers the following functions, among others:
- Event-based data model: This model captures very specific events that can take place on our website. For example, playing a video, buying a product or signing up for our newsletter.
- Advanced analysis functions: With these functions we can understand your behaviour on our website or certain general trends even better. For example, we can segment user groups, carry out comparative analyses of target groups or trace your journey or path on our website.
- Predictive modelling: On the basis of the data collected, missing data can be extrapolated through machine learning to predict future events and trends. This can help us develop better marketing strategies.
- Cross-platform analysis: Data can be collected and analysed from both websites and apps. This gives us the opportunity to analyse user behaviour across platforms, provided of course that you have consented to the data processing.
Why do we use Google Analytics on our website?
Our goal with this website is clear: we want to offer you the best possible service. The statistics and data from Google Analytics help us to achieve this goal.
The statistically evaluated data gives us a clear picture of the strengths and weaknesses of our website. On the one hand, we can optimise our site so that it is easier for interested people to find on Google. On the other hand, the data helps us to understand you as a visitor better. We therefore know very precisely what we need to improve on our website in order to offer you the best possible service. The data also helps us to carry out our advertising and marketing measures in a more individual and cost-effective way. After all, it only makes sense to show our products and services to people who are interested in them.
What data is stored by Google Analytics?
Using a tracking code, Google Analytics creates a random, unique ID that is linked to your browser cookie. This is how Google Analytics recognises you as a new user and a user ID is assigned to you. The next time you visit our site, you will be recognised as a “returning” user. All data collected is stored together with this user ID. Only this makes it possible to evaluate pseudonymous user profiles.
In order to analyse our website with Google Analytics, a property ID must be inserted into the tracking code. The data is then stored in the corresponding property. The Google Analytics 4 property is the default for every newly created property. Depending on the property used, data is stored for different lengths of time.
Identifiers such as cookies, app instance IDs, user IDs or custom event parameters are used to measure your interactions across platforms, provided you have given your consent. Interactions are all kinds of actions that you carry out on our website. If you also use other Google systems (such as a Google account), data generated via Google Analytics can be linked with third-party cookies. Google does not pass on any Google Analytics data unless we as the website operator authorise it. Exceptions may occur if this is required by law.
According to Google, no IP addresses are logged or stored in Google Analytics 4. However, Google uses the IP address data to derive location data and deletes it immediately afterwards. All IP addresses collected from users in the EU are therefore deleted before the data is stored in a data centre or on a server.
Since Google Analytics 4 focuses on event-based data, the tool uses significantly fewer cookies than previous versions (such as Google Universal Analytics). Nevertheless, there are some specific cookies that are used by GA4. These include, for example:
Name: _ga
Value: 2.1326744211.152113097992-5
Purpose: By default, analytics.js uses the cookie _ga to store the user ID. Basically, it serves to distinguish website visitors.
Expiry date: after 2 years
Name: _gid
Value: 2.1687193234.152113097992-1
Purpose: This cookie is also used to distinguish website visitors
Expiry date: after 24 hours
Name: _gat_gtag_UA_<property-id>
Value: 1
Purpose: Used to reduce the request rate. If Google Analytics is provided via Google Tag Manager, this cookie is named _dc_gtm_ <property-id>.
Expiry date: after 1 minute
Note: This list cannot claim to be complete, as Google repeatedly changes its choice of cookies. One goal of GA4 is also to improve data protection. The tool therefore offers several options for controlling data collection. For example, we can set the storage period ourselves and also control data collection.
Here we show you an overview of the most important types of data collected with Google Analytics:
Heatmaps: Google creates so-called heatmaps. Heatmaps show exactly those areas that you click on. This gives us information about where you are “moving around” on our site.
Session duration: Google refers to the time you spend on our site without leaving it as the session duration. If you have been inactive for 20 minutes, the session ends automatically.
Bounce rate : A bounce occurs when you only view one page on our website and then leave our website again.
Account creation: If you create an account or place an order on our website, Google Analytics collects this data.
Location: IP addresses are not logged or stored in Google Analytics. However, shortly before the IP address is deleted, derivations are used for location data.
Technical information: Technical information includes your browser type, your internet provider or your screen resolution, among other things.
Source of origin: Google Analytics, and of course we, are also interested in which website or which advertisement brought you to our site.
Other data includes contact details, any ratings, the playing of media (e.g. when you play a video via our site), the sharing of content via social media or adding to your favourites. The list does not claim to be complete and only serves as a general orientation on data storage by Google Analytics.
How long and where is the data stored?
Google has its servers distributed all over the world. Here you can read exactly where the Google data centres are located: https://datacenters.google/
Your data is distributed across different physical data carriers. This has the advantage that the data can be accessed more quickly and is better protected against manipulation. Every Google data centre has appropriate emergency programmes for your data. If, for example, hardware at Google fails or natural disasters paralyse servers, the risk of a service interruption at Google still remains low.
The retention period of the data depends on the properties used. The storage period is always defined separately for each individual property. Google Analytics offers us four options for controlling the storage period:
- 2 months: this is the shortest storage period.
- 14 months: by default, data remains stored in GA4 for 14 months.
- 26 months: data can also be stored for 26 months.
- Data is only deleted when we delete it manually
In addition, there is also the option that data is only deleted if you no longer visit our website within the period we have chosen. In this case, the retention period is reset each time you visit our website again within the specified period.
When the specified period has expired, the data is deleted once a month. This retention period applies to your data that is linked to cookies, user recognition and advertising IDs (e.g. cookies of the DoubleClick domain). Report results are based on aggregated data and are stored independently of user data. Aggregated data is a merging of individual data into a larger unit.
How can I delete my data or prevent data storage?
Under the data protection law of the European Union, you have the right to obtain information about your data and to update, delete or restrict it. With the browser add-on to deactivate Google Analytics JavaScript (analytics.js, gtag.js), you prevent Google Analytics 4 from using your data. You can download and install the browser add-on at https://tools.google.com/dlpage/gaoptout?hl=de . Please note that this add-on only deactivates data collection by Google Analytics.
If you generally want to deactivate, delete or manage cookies, you will find the corresponding links to the instructions for the most popular browsers in the section “Cookies”.
Legal basis
The use of Google Analytics requires your consent, which we have obtained with our cookie pop-up. According to Art. 6(1)(a) GDPR (consent) , this consent constitutes the legal basis for the processing of personal data as may occur when it is collected by web analytics tools.
In addition to consent, we have a legitimate interest in analysing the behaviour of website visitors and thus improving our offer technically and economically. With the help of Google Analytics, we recognise website errors, can identify attacks and improve economic efficiency. The legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use Google Analytics if you have given your consent.
Google also processes your data in the USA, among other places. Google is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data of EU citizens to the USA. You can find more information on this at https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
In addition, Google uses so-called standard contractual clauses (= Art. 46(2) and (3) GDPR). Standard contractual clauses (SCC) are templates provided by the EU Commission and are intended to ensure that your data also complies with European data protection standards when it is transferred to and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the standard contractual clauses, Google undertakes to comply with the European level of data protection when processing your relevant data, even if the data is stored, processed and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding standard contractual clauses here, among other places: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de
You can find the Google Ads Data Processing Terms, which refer to the standard contractual clauses, at https://business.safety.google/intl/de/adsprocessorterms/.
We hope we have been able to give you the most important information about data processing by Google Analytics. If you want to learn more about the tracking service, we recommend these two links: https://marketingplatform.google.com/about/analytics/terms/de/ and https://support.google.com/analytics/answer/6004245?hl=de.
If you want to learn more about data processing, use the Google privacy policy at https://policies.google.com/privacy?hl=de.
Data Processing Agreement (DPA) Google Analytics
We have concluded a data processing agreement (DPA) with Google within the meaning of Article 28 of the General Data Protection Regulation (GDPR). You can read exactly what a DPA is and, above all, what must be contained in a DPA in our general section “Data Processing Agreement (DPA)”.
This contract is required by law because Google processes personal data on our behalf. It clarifies that Google may only process data it receives from us according to our instructions and must comply with the GDPR. You can find the link to the data processing terms at https://business.safety.google/intl/de/adsprocessorterms/
Google Analytics Demographics and Interests Reports
We have activated the advertising reporting features in Google Analytics. The demographics and interests reports contain information on age, gender and interests. This allows us to get a better picture of our users – without being able to assign this data to individual persons. You can find out more about the advertising features at https://support.google.com/analytics/answer/3450482?hl=de_AT&utm_id=ad.
You can stop the use of the activities and information of your Google account under “Ad settings” at https://adssettings.google.com/authenticated by ticking a checkbox.
Google Analytics in Consent Mode
Depending on your consent, your personal data is processed by Google Analytics in the so-called consent mode. You can choose whether or not to agree to Google Analytics cookies. In doing so, you also choose which of your data Google Analytics may process. This collected data is mainly used to carry out measurements of user behaviour on the website, to serve targeted advertising and to provide us with web analysis reports. As a rule, you consent to data processing by Google via a cookie consent tool. If you do not consent to the data processing, only aggregated data is collected and processed. This means that data cannot be assigned to individual users and therefore no user profile of you is created. You can also only agree to statistical measurement. In this case, no personal data is processed and consequently it is not used for advertising or advertising performance measurement.
Google Analytics IP Anonymisation
We have implemented Google Analytics IP address anonymisation on this website. This function was developed by Google so that this website can comply with the applicable data protection regulations and recommendations of the local data protection authorities if they prohibit the storage of the full IP address. The anonymisation or masking of the IP takes place as soon as the IP addresses arrive in the Google Analytics data collection network and before the data is stored or processed.
You can find more information on IP anonymisation at https://support.google.com/analytics/answer/2763052?hl=de.
Google Optimize Privacy Policy
On our website we use Google Optimize, a website optimisation tool. The service provider is the American company Google Inc. For the European area, the company Google Ireland Limited (Gordon House, Barrow Street Dublin 4, Ireland) is responsible for all Google services.
Google also processes your data in the USA, among other places. Google is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data of EU citizens to the USA. You can find more information on this at https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
In addition, Google uses so-called standard contractual clauses (= Art. 46(2) and (3) GDPR). Standard contractual clauses (SCC) are templates provided by the EU Commission and are intended to ensure that your data also complies with European data protection standards when it is transferred to and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the standard contractual clauses, Google undertakes to comply with the European level of data protection when processing your relevant data, even if the data is stored, processed and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding standard contractual clauses here, among other places: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de
You can find the Google Ads Data Processing Terms, which refer to the standard contractual clauses, at https://business.safety.google/intl/de/adsprocessorterms/.
You can find out more about the data processed through the use of Google Optimize in the privacy policy at https://policies.google.com/privacy?hl=de.
Data Processing Agreement (DPA) Google Optimize
We have concluded a data processing agreement (DPA) with Google within the meaning of Article 28 of the General Data Protection Regulation (GDPR). You can read exactly what a DPA is and, above all, what must be contained in a DPA in our general section “Data Processing Agreement (DPA)”.
This contract is required by law because Google processes personal data on our behalf. It clarifies that Google may only process data it receives from us according to our instructions and must comply with the GDPR. You can find the link to the data processing terms at https://business.safety.google/intl/de/adsprocessorterms/
Google Site Kit Privacy Policy
|
Google Site Kit Privacy Policy Summary
👥 Data subjects: visitors to the website 🤝 Purpose: evaluation of visitor information to optimise the website. 📓 Data processed: access statistics containing data such as access locations, device data, access duration and time, navigation behaviour, click behaviour and IP addresses. You can find more details on this below and in the Google Analytics privacy policy. 📅 Storage period: depends on the properties used ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is Google Site Kit?
We have integrated the WordPress plugin Google Site Kit of the American company Google Inc. into our website. For the European area, the company Google Ireland Limited (Gordon House, Barrow Street Dublin 4, Ireland) is responsible for all Google services. With Google Site Kit we can quickly and easily view statistics from various Google products such as Google Analytics directly in our WordPress dashboard. The tool, or the tools integrated in Google Site Kit, also collect personal data from you, among other things. In this privacy policy we explain why we use Google Site Kit, how long and where data is stored and which other data protection texts are relevant to you in this context.
Google Site Kit is a plugin for the content management system WordPress. With this plugin we can view important statistics for website analysis directly in our dashboard. These are statistics collected by other Google products, above all by Google Analytics. In addition to Google Analytics, the services Google Search Console, Page Speed Insight, Google AdSense, Google Optimize and Google Tag Manager can also be linked with Google Site Kit.
Why do we use Google Site Kit on our website?
As a service provider, it is our job to offer you the best possible experience on our website. You should feel comfortable on our website and find exactly what you are looking for quickly and easily. Statistical evaluations help us to get to know you better and to adapt our offer to your wishes and interests. We use various Google tools for these evaluations. Site Kit makes our work much easier in this respect, because we can view and analyse the statistics of the Google products directly in the dashboard. We therefore no longer have to log in separately to each tool. Site Kit thus always provides a good overview of the most important analysis data.
What data is stored by Google Site Kit?
If you have actively consented to tracking tools in the cookie notice (also called script or banner), Google products such as Google Analytics set cookies and send data about you, for example about your user behaviour, to Google, where it is stored and processed. This also includes personal data such as your IP address.
For more detailed information on the individual services, we have separate text sections in this privacy policy. Take a look, for example, at our privacy policy on Google Analytics. There we go into great detail about the data collected. You will learn how long Google Analytics stores, manages and processes data, which cookies may be used and how you can prevent data storage. We also have separate privacy policies with comprehensive information for other Google services such as Google Tag Manager or Google AdSense.
Below we show you examples of Google Analytics cookies that can be set in your browser, provided you have generally agreed to data processing by Google. Please note that these cookies are only a selection:
Name: _ga
Value:2.1326744211.152113097992-2
Purpose: By default, analytics.js uses the cookie _ga to store the user ID. Basically, it serves to distinguish website visitors.
Expiry date: after 2 years
Name: _gid
Value:2.1687193234.152113097992-7
Purpose: This cookie also serves to distinguish website visitors.
Expiry date: after 24 hours
Name: _gat_gtag_UA_<property-id>
Value: 1
Purpose: This cookie is used to reduce the request rate.
Expiry date: after 1 minute
How long and where is the data stored?
Google stores collected data on its own Google servers, which are distributed worldwide. Most of the servers are located in the United States, so it is quite possible that your data will also be stored there. At https://datacenters.google/ you can see exactly where the company provides servers.
Data collected by Google Analytics is retained for a standard period of 26 months. Your user data is then deleted. The retention period applies to all data linked to cookies, user recognition and advertising IDs.
How can I delete my data or prevent data storage?
You always have the right to obtain information about your data and to have your data deleted, corrected or restricted. You can also deactivate, delete or manage cookies in your browser at any time.
If you generally want to deactivate, delete or manage cookies, you will find the corresponding links to the instructions for the most popular browsers in the section “Cookies”.
Legal basis
The use of Google Site Kit requires your consent, which we have obtained with our cookie pop-up. According to Art. 6(1)(a) GDPR (consent) , this consent constitutes the legal basis for the processing of personal data as may occur when it is collected by web analytics tools.
In addition to consent, we have a legitimate interest in analysing the behaviour of website visitors and thus improving our offer technically and economically. With the help of Google Site Kit, we recognise website errors, can identify attacks and improve economic efficiency. The legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use Google Site Kit if you have given your consent.
Google also processes your data in the USA, among other places. Google is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data of EU citizens to the USA. You can find more information on this at https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
In addition, Google uses so-called standard contractual clauses (= Art. 46(2) and (3) GDPR). Standard contractual clauses (SCC) are templates provided by the EU Commission and are intended to ensure that your data also complies with European data protection standards when it is transferred to and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the standard contractual clauses, Google undertakes to comply with the European level of data protection when processing your relevant data, even if the data is stored, processed and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding standard contractual clauses here, among other places: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de
You can find the Google Ads Data Processing Terms, which refer to the standard contractual clauses, at https://business.safety.google/intl/de/adsprocessorterms/.
To learn more about data processing by Google, we recommend Google's comprehensive privacy policy at https://policies.google.com/privacy?hl=de.
Content Delivery Networks Introduction
|
Content Delivery Networks Privacy Policy Summary
👥 Data subjects: visitors to the website 🤝 Purpose: optimising our service (so that the website can load faster) 📓 Data processed: data such as your IP address You can find more details on this below and in the individual data protection texts. 📅 Storage period: in most cases the data is stored until it is no longer needed to provide the service ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is a content delivery network?
On our website we use a so-called content delivery network. Usually such a network is simply called a CDN. A CDN helps us to load our website quickly and smoothly, regardless of your location. In the process, personal data of yours is also stored, managed and processed on the servers of the CDN provider used. Below we go into more detail about the service and its data processing in general. You can find detailed information about how your data is handled in the respective privacy policy of the provider.
Every content delivery network (CDN) is a network of regionally distributed servers, all connected to each other via the internet. Via this network, website content (especially very large files) can be delivered quickly and smoothly even during large load peaks. For this purpose, the CDN creates a copy of our website on its servers. Since these servers are distributed worldwide, the website can be delivered quickly. The data transfer to your browser is consequently significantly shortened by the CDN.
Why do we use a content delivery network for our website?
A fast-loading website is part of our service. We know, of course, how annoying it is when a website loads at a snail's pace. Usually you even lose patience and leave before the website has fully loaded. Of course we want to avoid that. That is why a fast-loading website is a matter of course in our website offering. With a content delivery network, our website loads much faster in your browser. The use of the CDN is particularly helpful when you are abroad, because the website is delivered from a server near you.
What data is processed?
When you request a website or the content of a website and this is cached in a CDN, the CDN forwards the request to the server closest to you, and that server delivers the content. Content delivery networks are structured in such a way that JavaScript libraries can be downloaded and are hosted on npm and GitHub servers. Alternatively, most CDNs can also load WordPress plugins if they are hosted on WordPress.org . Your browser may send personal data to the content delivery network we use. This includes data such as IP address, browser type, browser version, which web page is loaded or the time and date of the page visit. This data is collected and also stored by the CDN. Whether cookies are used for data storage depends on the network used. Please read the data protection texts of the respective service for this.
Right to object
If you want to completely prevent this data transfer, you can install a JavaScript blocker (see for example https://noscript.net/) on your PC. Of course, our website can then no longer offer the usual service (such as fast loading speed).
Legal basis
If you have consented to the use of a content delivery network, the legal basis for the corresponding data processing is this consent. According to Art. 6(1)(a) GDPR (consent) , this consent constitutes the legal basis for the processing of personal data as may occur when it is collected by a content delivery network.
We also have a legitimate interest in using a content delivery network to optimise our online service and make it more secure. The corresponding legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use the tool if you have given your consent.
Information on specific content delivery networks can be found – if available – in the following sections.
BootstrapCDN Privacy Policy
|
BootstrapCDN Privacy Policy Summary
👥 Data subjects: visitors to the website 🤝 Purpose: optimising our service (so that the website can load faster) 📓 Data processed: data such as your IP address, browser type, browser version, which web page is loaded or the time and date of the page visit You can find more details on this further down in this privacy policy. 📅 Storage period: in most cases the data is stored until it is no longer needed to provide the service ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is BootstrapCDN?
In order to deliver all our individual web pages (subpages of our website) to you quickly and securely on all devices, we use the content delivery network (CDN) BootstrapCDN, an open-source service of jsdelivr.com of the Polish software company ProspectOne, Królewska 65A/1, 30-081, Kraków, Poland. A content delivery network (CDN) is a network of regionally distributed servers that are connected to each other via the internet. Through this network, content, especially very large files, can be delivered quickly even during large load peaks.
Why do we use BootstrapCDN?
Of course, we want to offer you a comprehensive and well-functioning service with our website. This also includes a fast website. With the jsdelivr.com CDN, our website can be loaded much faster for you. The use of the jsdelivr.com CDN is particularly helpful for users from abroad, as the page can be delivered from a server nearby.
What data is processed by BootstrapCDN?
BootstrapCDN works by delivering so-called JavaScript libraries to your browser. When your browser downloads a file from BootstrapCDN, your IP address is transmitted during the connection to the Bootstrap CDN server. Personal data can therefore also be sent and stored. BootstrapCDN can thus collect and store user data such as IP address, browser type, browser version, which web page is loaded or the time and date of the page visit. In the privacy policy of BootstrapCDN or jsdelivr.com it is expressly pointed out that the company does not use cookies or other tracking services.
How long and where is the data stored?
BootstrapCDN has servers distributed in various countries, and your data may also be stored outside the European Economic Area. BootstrapCDN retains personal data processed on our behalf for as long as is necessary to provide the services offered and as is necessary to fulfil legal obligations, resolve disputes and enforce agreements.
Right to object
You always have the right to information, rectification and erasure of your personal data. If you have any questions, you can also contact those responsible at BootstrapCDN at any time.
If you want to prevent this data transfer, you can install a JavaScript blocker (see for example https://noscript.net/) or deactivate the execution of JavaScript code in your browser. Please note, however, that the website can then no longer offer the usual service (such as fast loading speed).
Legal basis
If you have consented to the use of BootstrapCDN, the legal basis for the corresponding data processing is this consent. According to Art. 6(1)(a) GDPR (consent) , this consent constitutes the legal basis for the processing of personal data as may occur when it is collected by BootstrapCDN.
We also have a legitimate interest in using BootstrapCDN to optimise our online service and make it more secure. The corresponding legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use BootstrapCDN if you have given your consent.
We point out that, according to the European Court of Justice, there is currently no adequate level of protection for data transfers to the USA. The data processing is essentially carried out by BootstrapCDN. This may result in data being processed and stored without anonymisation. Furthermore, US government authorities may be able to access individual data. It may also happen that this data is linked with data from other possible services of BootstrapCDN with which you have a user account.
You can find more information on data protection at BootstrapCDN at https://www.jsdelivr.com/terms/privacy-policy-jsdelivr-net.
Cloudflare Privacy Policy
|
Cloudflare Privacy Policy Summary
👥 Data subjects: visitors to the website 🤝 Purpose: optimising our service (so that the website can load faster) 📓 Data processed: data such as IP address, contact and log information, security fingerprints and performance data for websites You can find more details on this further down in this privacy policy. 📅 Storage period: in most cases the data is stored for less than 24 hours ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is Cloudflare?
On this website we use Cloudflare from Cloudflare, Inc. (101 Townsend St., San Francisco, CA 94107, USA) to make our website faster and more secure. Cloudflare uses cookies and processes user data. Cloudflare, Inc. is an American company that offers a content delivery network and various security services. These services sit between the user and our hosting provider. We try to explain in more detail below exactly what all this means.
A content delivery network (CDN), such as the one provided by Cloudflare, is nothing more than a network of connected servers. Cloudflare has such servers distributed all over the world in order to bring websites to your screen faster. Put simply, Cloudflare makes copies of our website and places them on its own servers. When you now visit our website, a load-balancing system ensures that the largest parts of our website are delivered by the server that can display our website to you the fastest. The data transmission route to your browser is significantly shortened by a CDN. This means that the content of our website is delivered to you by Cloudflare not only from our hosting server but from servers all over the world. The use of Cloudflare is particularly helpful for users from abroad, as the page can be delivered from a server nearby. In addition to delivering websites quickly, Cloudflare also offers various security services, such as DDoS protection or the web application firewall.
Why do we use Cloudflare on our website?
Of course, we want to offer you the best possible service with our website. Cloudflare helps us to make our website faster and more secure. Cloudflare offers us both web optimisations and security services such as DDoS protection and web firewall. This also includes a reverse proxy and the content delivery network (CDN). Cloudflare blocks threats and limits abusive bots and crawlers that waste our bandwidth and server resources. By storing our website in local data centres and blocking spam software, Cloudflare enables us to reduce our bandwidth usage by around 60%. Providing content via a data centre near you and some web optimisations carried out there reduce the average loading time of a website by around half. According to Cloudflare, the “I'm Under Attack Mode” setting can mitigate further attacks by displaying a JavaScript computing task that must be solved before a user can access a website. Overall, this makes our website significantly more powerful and less susceptible to spam or other attacks.
What data is processed by Cloudflare?
In general, Cloudflare only forwards data that is controlled by website operators. The content is therefore not determined by Cloudflare but always by the website operator itself. In addition, Cloudflare may collect certain information about the use of our website and process data sent by us or for which Cloudflare has received corresponding instructions. In most cases, Cloudflare receives data such as IP address, contact and log information, security fingerprints and performance data for websites. Log data helps Cloudflare, for example, to recognise new threats. In this way, Cloudflare can guarantee a high level of security protection for our website. Cloudflare processes this data as part of its services in compliance with applicable laws. This of course includes the General Data Protection Regulation (GDPR). Cloudflare also works with third-party providers. They may only process personal data under the instruction of Cloudflare and in accordance with the privacy policies and other confidentiality and security measures. Cloudflare does not pass on any personal data without our explicit consent.
How long and where is the data stored?
Cloudflare stores your information mainly in the USA and in the European Economic Area. Cloudflare can transfer and access the information described above from all over the world. In general, Cloudflare stores user-level data for domains in the Free, Pro and Business versions for less than 24 hours. For Enterprise domains that have activated Cloudflare Logs (formerly Enterprise LogShare or ELS), the data can be stored for up to 7 days. However, if IP addresses trigger security warnings at Cloudflare, there may be exceptions to the storage period stated above.
How can I delete my data or prevent data storage?
Cloudflare only retains data logs for as long as necessary, and in most cases this data is deleted again within 24 hours. Cloudflare also does not store any personal data, such as your IP address. However, there is information that Cloudflare stores indefinitely as part of its permanent logs in order to improve the overall performance of Cloudflare Resolver and to detect any security risks. You can read exactly which permanent logs are stored at https://www.cloudflare.com/application/privacypolicy/ . All data that Cloudflare collects (temporarily or permanently) is cleansed of all personal data. All permanent logs are also anonymised by Cloudflare.
In its privacy policy, Cloudflare states that it is not responsible for the content it receives. If, for example, you ask Cloudflare whether it can update or delete your content, Cloudflare generally refers you to us as the website operator. You can also completely prevent the entire collection and processing of your data by Cloudflare by deactivating the execution of script code in your browser or by integrating a script blocker into your browser.
Legal basis
If you have consented to the use of Cloudflare, the legal basis for the corresponding data processing is this consent. According to Art. 6(1)(a) GDPR (consent) , this consent constitutes the legal basis for the processing of personal data as may occur when it is collected by Cloudflare.
We also have a legitimate interest in using Cloudflare to optimise our online service and make it more secure. The corresponding legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use Cloudflare if you have given your consent.
Cloudflare also processes your data in the USA, among other places. Cloudflare is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data of EU citizens to the USA. You can find more information on this at https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
In addition, Cloudflare uses so-called standard contractual clauses (= Art. 46(2) and (3) GDPR). Standard contractual clauses (SCC) are templates provided by the EU Commission and are intended to ensure that your data also complies with European data protection standards when it is transferred to and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the standard contractual clauses, Cloudflare undertakes to comply with the European level of data protection when processing your relevant data, even if the data is stored, processed and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding standard contractual clauses here, among other places: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de.
You can find out more about the standard contractual clauses and the data processed through the use of Cloudflare in the privacy policy at https://www.cloudflare.com/de-de/privacypolicy/.
jQuery CDN Privacy Policy
|
jQuery CDN Privacy Policy Summary
👥 Data subjects: visitors to the website 🤝 Purpose: optimising our service (so that the website can load faster) 📓 Data processed: data such as your IP address You can find more details on this further down in this privacy policy. 📅 Storage period: in most cases the data is stored until it is no longer needed to provide the service ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is jQuery?
In order to deliver our website or the jQuery library to you quickly and smoothly on different devices, we use services of jQuery CDN of the company OpenJS Foundation. jQuery is distributed via the content delivery network (CDN) of the American software company Fastly, Inc. (475 Brannan St, Suite 300 San Francisco, CA 94107, USA). This service stores, manages and processes personal data of yours. In this privacy policy we go into more detail about which data of yours is processed through the use of jQuery CDN.
A content delivery network (CDN) is a network of regionally distributed servers that are connected to each other via the internet. Through this network, content, especially very large files, can be delivered quickly even during large load peaks. jQuery creates a copy of our website on its servers. In this way our website can be delivered as quickly as possible. This means that the data transmission to your browser is shortened by a CDN.
Why do we use jQuery on our website?
Of course, we want to offer you a comprehensive and well-functioning service with our website. This also includes a fast website. With jQuery, our website can be loaded much faster for you. The use of jQuery CDN is particularly helpful for users from abroad, as the page can be delivered from a server nearby.
What data is processed by jQuery?
jQuery uses JavaScript libraries to deliver our website content quickly. For this purpose, a CDN server loads the necessary files. As soon as a connection to the CDN server has been established, your IP address is recorded and stored. This only happens if this data has not already been stored in your browser by a previous website visit.
How long and where is the data stored?
jQuery or Fastly has servers distributed in various countries, and your data can therefore be stored both in America and in the European Economic Area. Fastly retains personal data processed on our behalf for as long as is necessary to provide the services offered and as is necessary to fulfil legal obligations, resolve disputes and enforce agreements.
Right to object
You always have the right to information, rectification and erasure of your personal data. If you have any questions, you can also contact those responsible at jQuery at any time.
If you do not want data to be transferred, you always have the option of installing JavaScript blockers such as https://www.ghostery.com/ or noscript.net . You can also simply deactivate the execution of JavaScript code in your browser. If you decide to deactivate JavaScript code, the usual functions will also change. For example, a website will no longer load as quickly.
Legal basis
If you have consented to the use of jQuery CDN, the legal basis for the corresponding data processing is this consent. According to Art. 6(1)(a) GDPR (consent) , this consent constitutes the legal basis for the processing of personal data as may occur when it is collected by jQuery CDN.
We also have a legitimate interest in using jQuery CDN to optimise our online service and make it more secure. The corresponding legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use the tool if you have given your consent.
Fastly also processes your data in the USA, among other places. Fastly is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data of EU citizens to the USA. You can find more information on this at https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
In addition, Fastly uses so-called standard contractual clauses (= Art. 46(2) and (3) GDPR). Standard contractual clauses (SCC) are templates provided by the EU Commission and are intended to ensure that your data also complies with European data protection standards when it is transferred to and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the standard contractual clauses, Fastly undertakes to comply with the European level of data protection when processing your relevant data, even if the data is stored, processed and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding standard contractual clauses here, among other places: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de.
You can find the Fastly Data Protection Terms, which correspond to the standard contractual clauses, at https://www.fastly.com/data-processing/.
You can find more information on data protection at Fastly at https://www.fastly.com/privacy/ and on jQuery at https://images.prismic.io/openjsf/ba00b254-685f-4e54-b1ca-17984b0f3e55_OpenJS-Foundation-Privacy-Policy-2019-11-15.pdf.
jsdelivr.com CDN Privacy Policy
|
jsdelivr.com CDN Privacy Policy Summary
👥 Data subjects: visitors to the website 🤝 Purpose: optimising our service (so that the website can load faster) 📓 Data processed: data such as your IP address, browser type, browser version, which web page is loaded or the time and date of the page visit You can find more details on this further down in this privacy policy. 📅 Storage period: in most cases the data is stored until it is no longer needed to provide the service ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is the jsdelivr.com CDN?
In order to deliver our individual web pages to you quickly and flawlessly on all different devices, we use the open-source services of jsdelivr.com of the Polish software company ProspectOne, Królewska 65A/1, 30-081, Kraków, Poland. This is a content delivery network (CDN). This is a network of regionally distributed servers connected via the internet. As a result, content, especially large files, can be delivered quickly and optimally even during large load peaks.
Why do we use the jsdelivr.com CDN?
Of course, we want to offer you a comprehensive and well-functioning service with our website. This also includes a fast website. With the jsdelivr.com CDN, our website can be loaded much faster for you. The use of the jsdelivr.com CDN is particularly helpful for users from abroad, as the page can be delivered from a server nearby.
What data is processed by the jsdelivr.com CDN?
jsDelivr is structured in such a way that JavaScript libraries hosted on npm and GitHub servers can be downloaded. However, WordPress plugins can also be loaded, provided they are hosted on WordPress.org . To provide this service, your browser may send personal data to jsdelivr.com . jsDelivr can thus collect and store user data such as IP address, browser type, browser version, which web page is loaded or the time and date of the page visit. In the privacy policy of jsdelivr.com it is expressly pointed out that the company does not use cookies or other tracking services.
How long and where is the data stored?
jsDelivr has servers distributed in various countries, and your data may also be stored outside the European Economic Area. jsDelivr retains personal data processed on our behalf for as long as is necessary to provide the services offered and as is necessary to fulfil legal obligations, resolve disputes and enforce agreements.
Right to object
You always have the right to information, rectification and erasure of your personal data. If you have any questions, you can also contact those responsible at the jsdelivr.com CDN at any time.
If you want to prevent this data transfer, you can install a JavaScript blocker (see for example https://noscript.net/) on your PC. Please note, however, that the website can then no longer offer the usual service (such as fast loading speed).
Legal basis
If you have consented to the use of the jsdelivr.com CDN, the legal basis for the corresponding data processing is this consent. According to Art. 6(1)(a) GDPR (consent) , this consent constitutes the legal basis for the processing of personal data as may occur when it is collected by the jsdelivr.com CDN.
We also have a legitimate interest in using the jsdelivr.com CDN to optimise our online service and make it more secure. The corresponding legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use the tool if you have given your consent.
You can find more detailed information on data processing by the software service jsDelivr in the company's privacy policy at https://www.jsdelivr.com/terms/privacy-policy-jsdelivr-net.
Cookie Consent Management Platform Introduction
|
Cookie Consent Management Platform Summary
👥 Data subjects: website visitors 🤝 Purpose: obtaining and managing consent to certain cookies and thus the use of certain tools 📓 Data processed: data for managing the cookie settings chosen, such as IP address, time of consent, type of consent, individual consents. You can find more details on this from the respective tool used. 📅 Storage period: depends on the tool used; you should expect periods of several years ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is a cookie consent management platform?
On our website we use consent management platform (CMP) software, which makes it easier for us and for you to handle the scripts and cookies used correctly and securely. The software automatically creates a cookie pop-up, scans and controls all scripts and cookies, provides you with the cookie consent required under data protection law and helps us and you keep track of all cookies. Most cookie consent management tools identify and categorise all existing cookies. You as a website visitor then decide for yourself whether and which scripts and cookies you allow or do not allow. The following graphic shows the relationship between browser, web server and CMP.
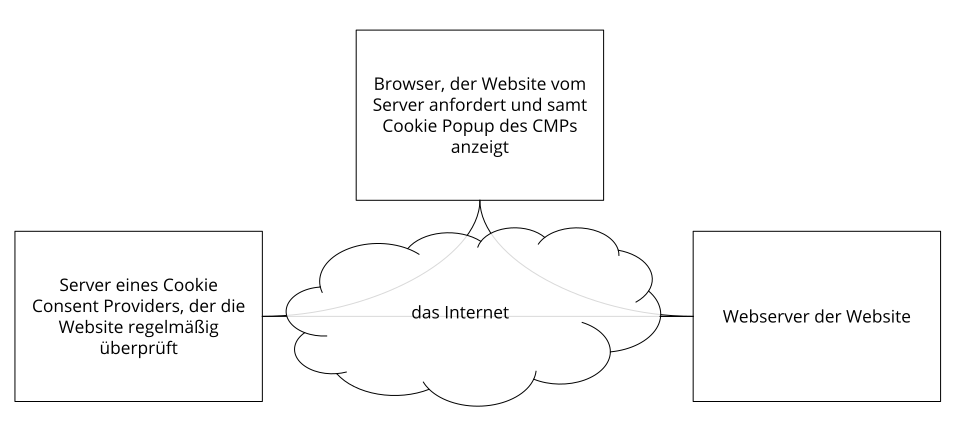
Why do we use a cookie management tool?
Our goal is to offer you the best possible transparency in the area of data protection. We are also legally obliged to do so. We want to inform you as well as possible about all tools and all cookies that can store and process your data. It is also your right to decide for yourself which cookies you accept and which you do not. In order to grant you this right, we first need to know exactly which cookies have ended up on our website at all. Thanks to a cookie management tool that regularly scans the website for all existing cookies, we know about all cookies and can provide you with GDPR-compliant information about them. Via the consent system you can then accept or reject cookies.
What data is processed?
Within our cookie management tool, you can manage each individual cookie yourself and have complete control over the storage and processing of your data. Your declaration of consent is stored so that we do not have to ask you every time you visit our website again and so that we can also prove your consent if legally required. This is stored either in an opt-in cookie or on a server. The storage period of your cookie consent varies depending on the provider of the cookie management tool. This data (such as pseudonymous user ID, time of consent, details of the cookie categories or tools, browser, device information) is usually stored for up to two years.
Duration of data processing
We will inform you about the duration of data processing below, provided we have further information on this. In general, we only process personal data for as long as is absolutely necessary to provide our services and products. Data stored in cookies is stored for different lengths of time. Some cookies are deleted as soon as you leave the website, others can be stored in your browser for several years. The exact duration of data processing depends on the tool used; in most cases you should expect a storage period of several years. The respective privacy policies of the individual providers usually contain precise information about the duration of data processing.
Right to object
You also have the right and the possibility to withdraw your consent to the use of cookies at any time. This works either via our cookie management tool or via other opt-out functions. For example, you can also prevent data collection by cookies by managing, deactivating or deleting cookies in your browser.
Information on specific cookie management tools can be found – if available – in the following sections.
Legal basis
If you agree to cookies, personal data of yours is processed and stored via these cookies. If, through your Consent (Article 6(1)(a) GDPR), we are permitted to use cookies, this consent is at the same time the legal basis for the use of cookies or the processing of your data. In order to be able to manage consent to cookies and to enable you to give consent, cookie consent management platform software is used. The use of this software enables us to operate the website efficiently and in compliance with the law, which constitutes a legitimate interest (Article 6(1)(f) GDPR).
Cookiebot Privacy Policy
|
Cookiebot Privacy Policy Summary
👥 Data subjects: website visitors 🤝 Purpose: obtaining consent to certain cookies and thus the use of certain tools 📓 Data processed: data for managing the cookie settings chosen, such as IP address, time of consent, type of consent, individual consents. You can find more details on this from the respective tool used. 📅 Storage period: the data is deleted after one year ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is Cookiebot?
On our website we use functions of the provider Cookiebot. The company behind Cookiebot is Cybot A/S, Havnegade 39, 1058 Copenhagen, DK. Among other things, Cookiebot offers us the possibility of providing you with a comprehensive cookie notice (also called cookie banner). By using this function, data of yours may be sent to, stored and processed by Cookiebot or Cybot. In this privacy policy we inform you why we use Cookiebot, which data is transferred and how you can prevent this data transfer.
Cookiebot is a software product of the company Cybot. The software automatically creates a GDPR-compliant cookie notice for our website visitors. In addition, the technology behind Cookiebot scans, controls and evaluates all cookies and tracking measures on our website.
Why do we use Cookiebot on our website?
We take data protection very seriously. We want to show you exactly what is happening on our website and which of your data is stored. Cookiebot helps us to get a good overview of all our cookies (first- and third-party cookies). This allows us to inform you precisely and transparently about the use of cookies on our website. You always receive an up-to-date and data-protection-compliant cookie notice and decide for yourself which cookies you allow and which you do not.
What data is stored by Cookiebot?
If you allow cookies, the following data is transferred to, stored and processed by Cybot.
- IP address (in anonymised form, the last 3 digits are set to 0)
- date and time of your consent
- our website URL
- technical browser data
- encrypted, anonymous key
- the cookies you have allowed (as proof of consent)
The following cookies are set by Cookiebot if you have agreed to the use of cookies:
Name: CookieConsent
Value: {stamp:’P7to4eNgIHvJvDerjKneBsmJQd9113097992-2
Purpose: Your consent status is stored in this cookie. This allows our website to read and follow the current status on future visits as well.
Expiry date: after one year
Name: CookieConsentBulkTicket
Value: kDSPWpA%2fjhljZKClPqsncfR8SveTnNWhys5NojaxdFYBPjZ2PaDnUw%3d%3113097992-6
Purpose: This cookie is set if you allow all cookies and have thus activated a “bulk consent”. The cookie then stores its own random and unique ID.
Expiry date: after one year
Note: Please bear in mind that this is an example list and we cannot claim it to be complete. In the cookie declaration at https://www.cookiebot.com/de/cookie-declaration/ you can see which other cookies may be used.
According to Cybot's privacy policy, the company does not sell personal data. However, Cybot passes on data to trustworthy third parties or subcontractors that help the company achieve its own business objectives. Data is also passed on if this is legally required.
How long and where is the data stored?
All data collected is transferred, stored and forwarded exclusively within the European Union. The data is stored in an Azure data centre (cloud provider is Microsoft). At https://azure.microsoft.com/de-de/explore/global-infrastructure/geographies/ you can find out more about all “Azure regions”. All user data is deleted by Cookiebot 12 months after registration (cookie consent) or immediately after termination of the Cookiebot service.
How can I delete my data or prevent data storage?
You have the right to access your personal data and also to delete it at any time. You can prevent data collection and storage, for example, by declining the use of cookies via the cookie notice. Your browser offers another way to prevent data processing or to manage it according to your wishes. Cookie management works slightly differently depending on the browser. In the section “Cookies” you will find the corresponding links to the instructions for the most popular browsers.
Legal basis
If you agree to cookies, personal data of yours is processed and stored via these cookies. If, through your Consent (Article 6(1)(a) GDPR), we are permitted to use cookies, this consent is at the same time the legal basis for the use of cookies or the processing of your data. In order to be able to manage consent to cookies and to enable you to give consent, Cookiebot is used. The use of this software enables us to operate the website efficiently and in compliance with the law, which constitutes a legitimate interest (Article 6(1)(f) GDPR).
If you want to learn more about the privacy policy of “Cookiebot” or the company behind it, Cybot, we recommend that you read the privacy policy at https://www.cookiebot.com/de/privacy-policy/ .
Security & Anti-Spam
|
Security & Anti-Spam Privacy Policy Summary
👥 Data subjects: visitors to the website 🤝 Purpose: cyber security 📓 Data processed: data such as your IP address, name or technical data such as browser version You can find more details on this below and in the individual data protection texts. 📅 Storage period: in most cases the data is stored until it is no longer needed to provide the service ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is security & anti-spam software?
With so-called security & anti-spam software, you and we can protect ourselves against various spam or phishing emails and possible other cyber attacks. Spam refers to mass-mailed advertising emails that you did not request yourself. Such emails are also called junk and can also cause costs. Phishing emails, on the other hand, are messages that aim to build trust via fake messages or websites in order to obtain personal data. Anti-spam software usually protects against unwanted spam messages or malicious emails that could, for example, introduce viruses into our system. We also use general firewall and security systems that protect our computers against unwanted network attacks.
Why do we use security & anti-spam software?
We place particular emphasis on security on our website. After all, it is not only about our security but above all about yours. Unfortunately, cyber threats have now become part of everyday life in the world of IT and the internet. Hackers often try to steal personal data from an IT system with the help of a cyber attack. That is why a good defence system is absolutely necessary. A security system monitors all incoming and outgoing connections to our network or computer. In order to achieve even greater security against cyber attacks, we also use other external security services in addition to the standardised security systems on our computer. This better prevents unauthorised data traffic, and in this way we protect ourselves against cybercrime.
What data is processed by security & anti-spam software?
Exactly which data is collected and stored naturally depends on the respective service. However, we always endeavour to use only programs that collect data very sparingly or only store data that is necessary to provide the service offered. In principle, the service may store data such as name, address, IP address, email address and technical data such as browser type or browser version. Performance and log data may also be collected in order to detect possible incoming threats in good time. This data is processed as part of the services and in compliance with applicable laws. For US providers (via the standard contractual clauses), this also includes the GDPR. In some cases these security services also work with third-party providers, which may store and/or process data under instruction and in accordance with the privacy policies and other security measures. Data is usually stored via cookies.
Duration of data processing
We will inform you about the duration of data processing below, provided we have further information on this. For example, security programs store data until you or we revoke the data storage. In general, personal data is only stored for as long as is absolutely necessary to provide the services. Unfortunately, in many cases we lack precise information from the providers about the length of storage.
Right to object
You also have the right and the possibility to withdraw your consent to the use of cookies or third-party security software providers at any time. This works either via our cookie management tool or via other opt-out functions. For example, you can also prevent data collection by cookies by managing, deactivating or deleting cookies in your browser.
Since cookies may also be used with such security services, we recommend our general privacy policy on cookies. To find out exactly which data of yours is stored and processed, you should read the privacy policies of the respective tools.
Legal basis
We use the security services mainly on the basis of our legitimate interests (Art. 6(1)(f) GDPR) in a good security system against various cyber attacks.
Certain processing operations, in particular the use of cookies and the use of security functions, require your consent. If you have consented to your data being processed and stored by integrated security services, this consent is the legal basis for the data processing (Art. 6(1)(a) GDPR). Most of the services we use set cookies in your browser to store data. We therefore recommend that you read our data protection text on cookies carefully and look at the privacy policy or cookie policies of the respective service provider.
Information on specific tools can be found – if available – in the following sections.
Google reCAPTCHA Privacy Policy
|
Google reCAPTCHA Privacy Policy Summary
👥 Data subjects: visitors to the website 🤝 Purpose: optimising our service and protecting against cyber attacks 📓 Data processed: data such as IP address, browser information, your operating system, limited location and usage data You can find more details on this further down in this privacy policy. 📅 Storage period: depends on the data stored ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is reCAPTCHA?
Our top priority is to secure and protect our website as well as possible for you and for us. To ensure this, we use Google reCAPTCHA from Google Inc. For the European area, the company Google Ireland Limited (Gordon House, Barrow Street Dublin 4, Ireland) is responsible for all Google services. With reCAPTCHA we can determine whether you really are a human being of flesh and blood and not a robot or other spam software. By spam we mean any unwanted information sent to us electronically without being requested. With the classic CAPTCHAs you usually had to solve text or picture puzzles for verification. With reCAPTCHA from Google we usually do not have to bother you with such puzzles. In most cases it is sufficient to simply tick a box and thus confirm that you are not a bot. With the new Invisible reCAPTCHA version you do not even have to tick a box any more. You will find out exactly how this works and, above all, which data is used for it in the course of this privacy policy.
reCAPTCHA is a free captcha service from Google that protects websites against spam software and misuse by non-human visitors. This service is most commonly used when you fill in forms on the internet. A captcha service is a kind of automatic Turing test intended to ensure that an action on the internet is carried out by a human and not by a bot. In the classic Turing test (named after the computer scientist Alan Turing), a human distinguishes between bot and human. With captchas, this is also done by the computer or a software program. Classic captchas work with small tasks that are easy for humans to solve but present considerable difficulties for machines. With reCAPTCHA you no longer have to actively solve puzzles. The tool uses modern risk techniques to distinguish humans from bots. Here you only have to tick the text field “I'm not a robot”, and with Invisible reCAPTCHA even that is no longer necessary. With reCAPTCHA, a JavaScript element is integrated into the source code, and the tool then runs in the background and analyses your user behaviour. From these user actions, the software calculates a so-called captcha score. Google uses this score to calculate, even before the captcha is entered, how likely it is that you are a human. reCAPTCHA, or captchas in general, are always used when bots could manipulate or misuse certain actions (such as registrations, surveys, etc.).
Why do we use reCAPTCHA on our website?
We only want to welcome humans of flesh and blood on our site. Bots or spam software of all kinds can safely stay at home. That is why we pull out all the stops to protect ourselves and to offer you the best possible user-friendliness. For this reason we use Google reCAPTCHA from Google. This way we can be fairly sure that we remain a “bot-free” website. By using reCAPTCHA, data is transmitted to Google to determine whether you really are a human. reCAPTCHA therefore serves the security of our website and, as a consequence, your security too. For example, without reCAPTCHA a bot could register as many email addresses as possible during a registration in order to subsequently “spam” forums or blogs with unwanted advertising content. With reCAPTCHA we can avoid such bot attacks.
What data is stored by reCAPTCHA?
reCAPTCHA collects personal data from users to determine whether the actions on our website really come from humans. The IP address and other data that Google needs for the reCAPTCHA service may therefore be sent to Google. Within the member states of the EU or other contracting states of the Agreement on the European Economic Area, IP addresses are almost always shortened beforehand, before the data ends up on a server in the USA. The IP address is not combined with other Google data unless you are logged in to your Google account while using reCAPTCHA. First, the reCAPTCHA algorithm checks whether Google cookies from other Google services (YouTube, Gmail, etc.) have already been placed in your browser. reCAPTCHA then sets an additional cookie in your browser and takes a snapshot of your browser window.
The following list of collected browser and user data does not claim to be complete. Rather, these are examples of data which, to our knowledge, are processed by Google.
- Referrer URL (the address of the page from which the visitor comes)
- IP address (e.g. 256.123.123.1)
- Information about the operating system (the software that enables your computer to operate. Well-known operating systems are Windows, Mac OS X or Linux)
- Cookies (small text files that store data in your browser)
- Mouse and keyboard behaviour (every action you carry out with the mouse or keyboard is stored)
- Date and language settings (the language or date you have preset on your PC is stored)
- All JavaScript objects (JavaScript is a programming language that allows websites to adapt to the user. JavaScript objects can collect all kinds of data under one name)
- Screen resolution (shows how many pixels the image display consists of)
It is undisputed that Google uses and analyses this data even before you click on the “I'm not a robot” tick box. With the Invisible reCAPTCHA version, even ticking the box is no longer necessary and the entire recognition process runs in the background. Google does not tell you in detail how much and which data it stores.
The following cookies are used by reCAPTCHA: here we refer to the reCAPTCHA demo version from Google at https://www.google.com/recaptcha/api2/demo. All these cookies require a unique identifier for tracking purposes. Here is a list of cookies that Google reCAPTCHA set on the demo version:
Name: IDE
Value: WqTUmlnmv_qXyi_DGNPLESKnRNrpgXoy1K-pAZtAkMbHI-113097992-8
Purpose: This cookie is set by the company DoubleClick (also owned by Google) to register and report a user's actions on the website when interacting with advertisements. This allows the effectiveness of advertising to be measured and appropriate optimisation measures to be taken. IDE is stored in browsers under the domain doubleclick.net.
Expiry date: after one year
Name: 1P_JAR
Value: 2019-5-14-12
Purpose: This cookie collects statistics on website usage and measures conversions. A conversion occurs, for example, when a user becomes a buyer. The cookie is also used to display relevant advertisements to users. Furthermore, the cookie can be used to prevent a user from seeing the same advertisement more than once.
Expiry date: after one month
Name: ANID
Value: U7j1v3dZa1130979920xgZFmiqWppRWKOr
Purpose: We were unable to find out much information about this cookie. In Google's privacy policy, the cookie is mentioned in connection with “advertising cookies” such as “DSID”, “FLC”, “AID”, “TAID”. ANID is stored under the domain google.com.
Expiry date: after 9 months
Name: CONSENT
Value: YES+AT.de+20150628-20-0
Purpose: The cookie stores the status of a user's consent to the use of various Google services. CONSENT also serves security purposes, to verify users, prevent login credential fraud and protect user data from unauthorised attacks.
Expiry date: after 19 years
Name: NID
Value: 0WmuWqy113097992zILzqV_nmt3sDXwPeM5Q
Purpose: NID is used by Google to tailor advertisements to your Google search. With the help of the cookie, Google “remembers” your most frequently entered search queries or your previous interaction with ads. This way you always receive tailor-made advertisements. The cookie contains a unique ID to collect the user's personal settings for advertising purposes.
Expiry date: after 6 months
Name: DV
Value: gEAABBCjJMXcI0dSAAAANbqc113097992-4
Purpose: As soon as you have ticked the “I'm not a robot” box, this cookie is set. The cookie is used by Google Analytics for personalised advertising. DV collects information in anonymised form and is also used to distinguish between users.
Expiry date: after 10 minutes
Note: This list cannot claim to be complete, as experience shows that Google repeatedly changes its choice of cookies.
How long and where is the data stored?
By inserting reCAPTCHA, data of yours is transferred to the Google server. Even after repeated enquiries, Google does not make it clear exactly where this data is stored. Without having received confirmation from Google, it can be assumed that data such as mouse interaction, time spent on the website or language settings are stored on the European or American Google servers. The IP address that your browser transmits to Google is generally not merged with other Google data from other Google services. However, if you are logged in to your Google account while using the reCAPTCHA plug-in, the data will be merged. Google's differing data protection provisions apply to this.
How can I delete my data or prevent data storage?
If you do not want any data about you and your behaviour to be transmitted to Google, you must log out of Google completely and delete all Google cookies before visiting our website or using the reCAPTCHA software. In principle, the data is automatically transmitted to Google as soon as you call up our site. To delete this data again, you must contact Google support at https://support.google.com/?hl=de&tid=113097992 .
So if you use our website, you agree that Google LLC and its representatives automatically collect, process and use data.
Please note that when this tool is used, your data may also be stored and processed outside the EU. Most third countries (including the USA) are not considered secure under current European data protection law. Data may therefore not simply be transferred to, stored and processed in insecure third countries unless there are suitable guarantees (such as EU standard contractual clauses) between us and the non-European service provider.
Legal basis
If you have consented to the use of Google reCAPTCHA, the legal basis for the corresponding data processing is this consent. According to Art. 6(1)(a) GDPR (consent) , this consent constitutes the legal basis for the processing of personal data as may occur when it is collected by Google reCAPTCHA.
We also have a legitimate interest in using Google reCAPTCHA to optimise our online service and make it more secure. The corresponding legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use Google reCAPTCHA if you have given your consent.
Google also processes your data in the USA, among other places. Google is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data of EU citizens to the USA. You can find more information on this at https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
In addition, Google uses so-called standard contractual clauses (= Art. 46(2) and (3) GDPR). Standard contractual clauses (SCC) are templates provided by the EU Commission and are intended to ensure that your data also complies with European data protection standards when it is transferred to and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the standard contractual clauses, Google undertakes to comply with the European level of data protection when processing your relevant data, even if the data is stored, processed and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding standard contractual clauses here, among other places: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de
You can find the Google Ads Data Processing Terms, which refer to the standard contractual clauses, at https://business.safety.google/intl/de/adsprocessorterms/.
You can find out a little more about reCAPTCHA on Google's web developer site at https://developers.google.com/recaptcha/. Although Google goes into more detail about the technical development of reCAPTCHA here, you will search in vain there for precise information on data storage and data protection topics. You can find a good overview of the basic use of data at Google in its own privacy policy at https://policies.google.com/privacy.
Web Design Introduction
|
Web Design Privacy Policy Summary
👥 Data subjects: visitors to the website 🤝 Purpose: improving the user experience 📓 Data processed: which data is processed depends heavily on the services used. Usually it is IP address, technical data, language settings, browser version, screen resolution and name of the browser. You can find more details on this from the respective web design tools used. 📅 Storage period: depends on the tools used ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is web design?
On our website we use various tools that serve our web design. Web design is not just about our website looking nice, as is often assumed, but also about functionality and performance. But of course the right look of a website is also one of the major goals of professional web design. Web design is a sub-area of media design and deals with the visual as well as the structural and functional design of a website. The aim is to use web design to improve your experience on our website. In web design jargon, this is referred to as user experience (UX) and usability. User experience means all the impressions and experiences that the website visitor has on a website. A sub-item of user experience is usability. This is about the user-friendliness of a website. The main emphasis here is on content, subpages or products being clearly structured so that you can find what you are looking for easily and quickly. In order to offer you the best possible experience on our website, we also use so-called web design tools from third-party providers. The category “web design” in this privacy policy therefore includes all services that improve the design of our website. These can be, for example, fonts, various plugins or other integrated web design functions.
Why do we use web design tools?
How you take in information on a website depends very much on the structure, functionality and visual perception of the website. That is why good and professional web design has become increasingly important for us too. We are constantly working on improving our website and also see this as an extended service for you as a website visitor. Furthermore, a beautiful and functioning website also has economic advantages for us. After all, you will only visit us and make use of our offers if you feel completely comfortable.
What data is stored by web design tools?
When you visit our website, web design elements may be integrated into our pages that can also process data. Exactly which data this is naturally depends heavily on the tools used. Below you can see exactly which tools we use for our website. For more detailed information on data processing, we also recommend that you read the respective privacy policies of the tools used. There you will usually find out which data is processed, whether cookies are used and how long the data is retained. Fonts such as Google Fonts, for example, also automatically transmit information such as language settings, IP address, browser version, browser screen resolution and browser name to the Google servers.
Duration of data processing
How long data is processed is very individual and depends on the web design elements used. If cookies are used, for example, the retention period can be only one minute but also a few years. Please inform yourself about this. For this purpose we recommend, on the one hand, our general text section on cookies and the privacy policies of the tools used. There you will usually find out exactly which cookies are used and which information is stored in them. Google Font files, for example, are stored for one year. This is intended to improve the loading time of a website. In principle, data is only ever retained for as long as is necessary to provide the service. In the case of legal requirements, data may also be stored for longer.
Right to object
You also have the right and the possibility to withdraw your consent to the use of cookies or third-party providers at any time. This works either via our cookie management tool or via other opt-out functions. You can also prevent data collection by cookies by managing, deactivating or deleting cookies in your browser. However, with web design elements (mostly fonts) there is also data that cannot be deleted quite so easily. This is the case when data is automatically collected directly when a page is called up and transmitted to a third-party provider (such as Google). In that case please contact the support of the relevant provider. In the case of Google, you can reach support at https://support.google.com/?hl=de.
Legal basis
If you have consented to the use of web design tools, the legal basis for the corresponding data processing is this consent. According to Art. 6(1)(a) GDPR (consent), this consent constitutes the legal basis for the processing of personal data as may occur when it is collected by web design tools. We also have a legitimate interest in improving the web design on our website. After all, only then can we provide you with a beautiful and professional web offering. The corresponding legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use web design tools if you have given your consent. We definitely want to emphasise this again here.
Information on specific web design tools can be found – if available – in the following sections.
Adobe Fonts Privacy Policy
On our website we use Adobe Fonts, a web font hosting service. The service provider is the American company Adobe Inc. For the European area, the Irish company Adobe Systems Software Ireland Companies, 4-6 Riverwalk, Citywest Business Campus, Dublin 24, Ireland, is responsible.
Adobe also processes your data in the USA, among other places. Adobe is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data of EU citizens to the USA. You can find more information on this at https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
In addition, Adobe uses so-called standard contractual clauses (= Art. 46(2) and (3) GDPR). Standard contractual clauses (SCC) are templates provided by the EU Commission and are intended to ensure that your data also complies with European data protection standards when it is transferred to and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the standard contractual clauses, Adobe undertakes to comply with the European level of data protection when processing your relevant data, even if the data is stored, processed and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding standard contractual clauses here, among other places: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de
You can find more information on the standard contractual clauses at Adobe at https://www.adobe.com/at/privacy/eudatatransfers.html.
You can find out more about the data processed through the use of Adobe Fonts in the privacy policy at https://www.adobe.com/at/privacy.html .
Font Awesome Privacy Policy
|
Font Awesome Privacy Policy Summary
👥 Data subjects: visitors to the website 🤝 Purpose: optimising our service 📓 Data processed: such as IP address and which icon files are loaded You can find more details on this further down in this privacy policy. 📅 Storage period: files in identifiable form are stored for a few weeks ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is Font Awesome?
On our website we use Font Awesome from the American company Fonticons (307 S. Main St., Suite 202, Bentonville, AR 72712, USA). When you call up one of our web pages, the web font Font Awesome (specifically icons) is loaded via the Font Awesome content delivery network (CDN). This ensures that the texts or fonts and icons are displayed properly on every device. In this privacy policy we go into more detail about data storage and data processing by this service.
Icons play an increasingly important role for websites. Font Awesome is a web font developed specifically for web designers and web developers. With Font Awesome, icons, for example, can be scaled and coloured as desired using the stylesheet language CSS. They thus replace old image icons. The Font Awesome CDN is the easiest way to load the icons or fonts onto your website. To do this, we only had to integrate a small line of code into our website.
Why do we use Font Awesome on our website?
Font Awesome allows content on our website to be presented better. This helps you find your way around our website and grasp the content more easily. The icons can sometimes even replace whole words and save space. This is particularly practical when we optimise content specifically for smartphones. These icons are inserted as HTML code instead of images. This allows us to edit the icons with CSS exactly as we want. At the same time, Font Awesome also improves our loading speed, because these are only HTML elements and not icon images. All these advantages help us to make the website even clearer, fresher and faster for you.
What data is stored by Font Awesome?
The Font Awesome content delivery network (CDN) is used to load icons and symbols. CDNs are networks of servers distributed worldwide that make it possible to load files quickly from nearby. So as soon as you call up one of our pages, the corresponding icons are provided by Font Awesome.
In order for the web fonts to be loaded, your browser must establish a connection to the servers of the company Fonticons, Inc. In the process, your IP address is recognised. Font Awesome also collects data on which icon files are downloaded and when. Technical data such as your browser version, screen resolution or the time the page was called up is also transmitted.
This data is collected and stored for the following reasons:
- to optimise content delivery networks
- to detect and fix technical errors
- to protect CDNs from misuse and attacks
- to be able to calculate fees for Font Awesome Pro customers
- to find out the popularity of icons
- to know which computer and which software you use
If your browser does not allow web fonts, a standard font on your PC is automatically used. To the best of our current knowledge, no cookies are set. We are in contact with the data protection department of Font Awesome and will let you know as soon as we find out more.
How long and where is the data stored?
Font Awesome stores data on the use of the content delivery network on servers, including in the United States of America. However, the CDN servers are located worldwide and store user data where you are. In identifiable form, the data is usually only stored for a few weeks. Aggregated statistics on the use of the CDNs may also be stored for longer. Personal data is not included here.
How can I delete my data or prevent data storage?
To the best of our current knowledge, Font Awesome does not store any personal data via the content delivery networks. If you do not want data about the icons used to be stored, unfortunately you cannot visit our website. If your browser does not allow web fonts, no data is transmitted or stored either. In this case, the standard font of your computer is simply used.
Legal basis
If you have consented to the use of Font Awesome, the legal basis for the corresponding data processing is this consent. According to Art. 6(1)(a) GDPR (consent) , this consent constitutes the legal basis for the processing of personal data as may occur when it is collected by Font Awesome.
We also have a legitimate interest in using Font Awesome to optimise our online service. The corresponding legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use Font Awesome if you have given your consent.
We point out that, according to the European Court of Justice, there is currently no adequate level of protection for data transfers to the USA. The data processing is essentially carried out by Font Awesome. This may result in data being processed and stored without anonymisation. Furthermore, US government authorities may be able to access individual data. It may also happen that this data is linked with data from other possible services of Font Awesome with which you have a user account.
If you want to find out more about Font Awesome and how it handles data, we recommend the privacy policy at https://fontawesome.com/privacy and the help page at https://fontawesome.com/support.
Google Fonts Privacy Policy
|
Google Fonts Privacy Policy Summary
👥 Data subjects: visitors to the website 🤝 Purpose: optimising our service 📓 Data processed: data such as IP address and CSS and font requests You can find more details on this further down in this privacy policy. 📅 Storage period: font files are stored by Google for one year ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What are Google Fonts?
On our website we use Google Fonts. These are the “Google fonts” of Google Inc. For the European area, the company Google Ireland Limited (Gordon House, Barrow Street Dublin 4, Ireland) is responsible for all Google services.
You do not have to log in or provide a password to use Google fonts. Furthermore, no cookies are stored in your browser. The files (CSS, fonts) are requested via the Google domains fonts.googleapis.com and fonts.gstatic.com. According to Google, the requests for CSS and fonts are completely separate from all other Google services. If you have a Google account, you do not need to worry that your Google account data will be transmitted to Google while using Google Fonts. Google records the use of CSS (Cascading Style Sheets) and the fonts used and stores this data securely. We will look at exactly what the data storage looks like in detail.
Google Fonts (formerly Google Web Fonts) is a directory of over 800 fonts that Google makes available to its users free of charge.
Many of these fonts are published under the SIL Open Font License, while others have been published under the Apache license. Both are free software licences.
Why do we use Google Fonts on our website?
With Google Fonts we can use fonts on our own website without having to upload them to our own server. Google Fonts is an important building block for keeping the quality of our website high. All Google fonts are automatically optimised for the web, which saves data volume and is a great advantage especially for use on mobile devices. When you visit our site, the small file size ensures a fast loading time. Furthermore, Google Fonts are secure web fonts. Different image synthesis systems (rendering) in different browsers, operating systems and mobile devices can lead to errors. Such errors can visually distort texts or entire web pages. Thanks to the fast content delivery network (CDN), there are no cross-platform problems with Google Fonts. Google Fonts supports all common browsers (Google Chrome, Mozilla Firefox, Apple Safari, Opera) and works reliably on most modern mobile operating systems, including Android 2.2+ and iOS 4.2+ (iPhone, iPad, iPod). We therefore use Google Fonts so that we can present our entire online service as beautifully and uniformly as possible.
What data is stored by Google?
When you visit our website, the fonts are reloaded via a Google server. Through this external call, data is transmitted to the Google servers. This is also how Google recognises that you or your IP address is visiting our website. The Google Fonts API was developed to reduce the use, storage and collection of end-user data to what is necessary for the proper provision of fonts. API, by the way, stands for “Application Programming Interface” and serves, among other things, as a data transmitter in the software field.
Google Fonts stores CSS and font requests securely at Google and is therefore protected. Through the usage figures collected, Google can determine how well the individual fonts are received. Google publishes the results on internal analysis pages, such as Google Analytics. In addition, Google also uses data from its own web crawler to determine which websites use Google fonts. This data is published in the Google Fonts BigQuery database. Entrepreneurs and developers use the Google web service BigQuery to be able to examine and move large amounts of data.
However, it should also be borne in mind that with every Google Font request, information such as language settings, IP address, browser version, browser screen resolution and browser name is automatically transmitted to the Google servers. Whether this data is also stored cannot be clearly determined or is not clearly communicated by Google.
How long and where is the data stored?
Google stores requests for CSS assets for one day on its servers, which are mainly located outside the EU. This allows us to use the fonts with the help of a Google stylesheet. A stylesheet is a style template that can be used to quickly and easily change, for example, the design or font of a website.
The font files are stored by Google for one year. Google's aim is to improve the loading time of websites in general. If millions of websites refer to the same fonts, they are cached after the first visit and reappear immediately on all other websites visited later. Sometimes Google updates font files to reduce the file size, increase language coverage and improve the design.
How can I delete my data or prevent data storage?
The data that Google stores for one day or one year cannot simply be deleted. The data is automatically transmitted to Google when the page is called up. In order to be able to delete this data prematurely, you must contact Google support at https://support.google.com/?hl=de&tid=113097992 . In this case, you can only prevent data storage by not visiting our site.
Unlike other web fonts, Google allows us unrestricted access to all fonts. We can therefore access a sea of fonts without limit and thus get the best out of our website. You can find more about Google Fonts and other questions at https://developers.google.com/fonts/faq?tid=113097992. Although Google addresses data protection issues there, it does not contain really detailed information about data storage. It is relatively difficult to obtain really precise information about stored data from Google.
Legal basis
If you have consented to the use of Google Fonts, the legal basis for the corresponding data processing is this consent. According to Art. 6(1)(a) GDPR (consent) , this consent constitutes the legal basis for the processing of personal data as may occur when it is collected by Google Fonts.
We also have a legitimate interest in using Google Fonts to optimise our online service. The corresponding legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use Google Fonts if you have given your consent.
Google also processes your data in the USA, among other places. Google is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data of EU citizens to the USA. You can find more information on this at https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
In addition, Google uses so-called standard contractual clauses (= Art. 46(2) and (3) GDPR). Standard contractual clauses (SCC) are templates provided by the EU Commission and are intended to ensure that your data also complies with European data protection standards when it is transferred to and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the standard contractual clauses, Google undertakes to comply with the European level of data protection when processing your relevant data, even if the data is stored, processed and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding standard contractual clauses here, among other places: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de
You can find the Google Ads Data Processing Terms, which refer to the standard contractual clauses, at https://business.safety.google/intl/de/adsprocessorterms/.
You can also read which data is generally collected by Google and what this data is used for at https://www.google.com/intl/de/policies/privacy/ .
Google Fonts Local Privacy Policy
On our website we use Google Fonts of Google Inc. For the European area, the company Google Ireland Limited (Gordon House, Barrow Street Dublin 4, Ireland) is responsible. We have integrated the Google fonts locally, i.e. on our web server – not on Google's servers. As a result, there is no connection to Google servers and therefore no data transmission or storage.
What are Google Fonts?
Google Fonts used to be called Google Web Fonts. It is an interactive directory of over 800 fonts that Google provides free of charge. With Google Fonts you could use fonts without uploading them to your own server. However, in order to prevent any transfer of information to Google servers in this respect, we have downloaded the fonts to our server. In this way we act in compliance with data protection law and do not pass on any data to Google Fonts.
Online Map Services Introduction
|
Online Map Services Privacy Policy Summary
👥 Data subjects: visitors to the website 🤝 Purpose: improving the user experience 📓 Data processed: which data is processed depends heavily on the services used. Usually it is IP address, location data, search items and/or technical data. You can find more details on this from the respective tools used. 📅 Storage period: depends on the tools used ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What are online map services?
As an extended service, we also use online map services for our website. Google Maps is probably the service you know best, but there are also other providers that specialise in creating digital maps. Such services make it possible to display locations, route plans or other geographical information directly via our website. With an integrated map service, you no longer have to leave our website to view the route to a location, for example. In order for the online map to work on our website, map sections are integrated using HTML code. The services can then display road maps, the earth's surface or aerial or satellite images. If you use the built-in map offer, data is also transferred to the tool used and stored there. This data may also include personal data.
Why do we use online map services on our website?
Generally speaking, it is our concern to offer you a pleasant time on our website. And of course your time is only pleasant if you can find your way around our website easily and find all the information you need quickly and easily. That is why we thought an online map system could significantly optimise our service on the website. Without leaving our website, you can easily view route descriptions, locations or even sights with the help of the map system. Of course, it is also super practical that you can see at a glance where our company headquarters is located, so that you can find us quickly and safely. As you can see, there are simply many advantages, and we clearly regard online map services on our website as part of our customer service.
What data is stored by online map services?
When you open a page on our website that has an online map function built in, personal data may be transmitted to the respective service and stored there. Usually this is your IP address, which can also be used to determine your approximate location. In addition to the IP address, data such as search terms entered and longitude and latitude coordinates are also stored. If, for example, you enter an address for route planning, this data is also stored. The data is not stored by us but on the servers of the integrated tools. You can imagine it roughly like this: although you are on our website, when you interact with a map service this interaction actually takes place on their website. In order for the service to work properly, at least one cookie is usually also set in your browser. Google Maps, for example, also uses cookies to record user behaviour and thus optimise its own service and be able to serve personalised advertising. You can find out more about cookies in our section “Cookies”.
How long and where is the data stored?
Each online map service processes different user data. If we have further information, we will inform you about the duration of data processing further below in the corresponding sections on the individual tools. In principle, personal data is only ever retained for as long as is necessary to provide the service. Google Maps, for example, stores certain data for a fixed period, while you have to delete other data yourself. With Mapbox, for example, the IP address is retained for 30 days and then deleted. As you can see, each tool stores data for different lengths of time. We therefore recommend that you look carefully at the privacy policies of the tools used.
The providers also use cookies to store data about your user behaviour with the map service. You can find more general information about cookies in our section “Cookies”, but you can also find out in the data protection texts of the individual providers which cookies may be used. In most cases, however, this is only an example list and is not complete.
Right to object
You always have the possibility and also the right to access your personal data and to object to its use and processing. You can also withdraw the consent you have given us at any time. As a rule, the easiest way to do this is via the cookie consent tool. However, there are also other opt-out tools that you can use. You can also manage, delete or deactivate possible cookies set by the providers used yourself with just a few mouse clicks. However, it may then happen that some functions of the service no longer work as usual. How you manage cookies in your browser also depends on the browser you use. In the section “Cookies” you will also find links to the instructions for the most important browsers.
Legal basis
If you have consented to the use of an online map service, the legal basis for the corresponding data processing is this consent. According to Art. 6(1)(a) GDPR (consent), this consent constitutes the legal basis for the processing of personal data as may occur when it is collected by an online map service.
We also have a legitimate interest in using an online map service to optimise our service on our website. The corresponding legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). However, we only ever use an online map service if you have given your consent. We definitely want to state this again at this point.
Information on specific online map services can be found – if available – in the following sections.
Google Maps Privacy Policy
|
Google Maps Privacy Policy Summary
👥 Data subjects: visitors to the website 🤝 Purpose: optimising our service 📓 Data processed: data such as search terms entered, your IP address and also the latitude and longitude coordinates. You can find more details on this further down in this privacy policy. 📅 Storage period: depends on the data stored ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is Google Maps?
On our website we use Google Maps of Google Inc. For the European area, the company Google Ireland Limited (Gordon House, Barrow Street Dublin 4, Ireland) is responsible for all Google services. With Google Maps we can show you locations better and thus adapt our service to your needs. By using Google Maps, data is transferred to Google and stored on Google's servers. Here we want to go into more detail about what Google Maps is, why we use this Google service, which data is stored and how you can prevent this.
Google Maps is an internet map service of the company Google. With Google Maps you can search online via a PC, tablet or app for exact locations of cities, sights, accommodation or companies. If companies are represented on Google My Business, further information about the company is displayed in addition to the location. To show how to get there, map sections of a location can be integrated into a website using HTML code. Google Maps shows the earth's surface as a road map or as an aerial or satellite image. Thanks to the Street View images and the high-quality satellite images, very precise representations are possible.
Why do we use Google Maps on our website?
All our efforts on this site pursue the goal of offering you a useful and meaningful time on our website. By integrating Google Maps, we can provide you with the most important information on various locations. You can see at a glance where our company headquarters is located. The route description always shows you the best or fastest way to us. You can call up directions for routes by car, by public transport, on foot or by bicycle. For us, providing Google Maps is part of our customer service.
What data is stored by Google Maps?
In order for Google Maps to be able to offer its service in full, the company must collect and store data from you. This includes, among other things, the search terms entered, your IP address and also the latitude and longitude coordinates. If you use the route planner function, the start address entered is also stored. However, this data storage takes place on the Google Maps websites. We can only inform you about this but cannot exert any influence. Because we have integrated Google Maps into our website, Google sets at least one cookie (name: NID) in your browser. This cookie stores data about your user behaviour. Google uses this data primarily to optimise its own services and to provide individual, personalised advertising for you.
The following cookie is set in your browser due to the integration of Google Maps:
Name: NID
Value: 188=h26c1Ktha7fCQTx8rXgLyATyITJ113097992-5
Purpose: NID is used by Google to tailor advertisements to your Google search. With the help of the cookie, Google “remembers” your most frequently entered search queries or your previous interaction with ads. This way you always receive tailor-made advertisements. The cookie contains a unique ID that Google uses to collect your personal settings for advertising purposes.
Expiry date: after 6 months
Note: We cannot guarantee completeness in the information on the data stored. Especially with the use of cookies, changes can never be ruled out. To identify the cookie NID, a separate test page was created on which only Google Maps was integrated.
How long and where is the data stored?
The Google servers are located in data centres all over the world. However, most servers are located in America. For this reason, your data is increasingly stored in the USA. Here you can read exactly where the Google data centres are located: https://datacenters.google/
Google distributes the data across different data carriers. This makes the data quicker to retrieve and better protects it against any manipulation attempts. Each data centre also has special emergency programmes. If, for example, there are problems with Google hardware or a natural disaster paralyses the servers, the data still remains fairly securely protected.
Google stores some data for a fixed period. For other data, Google merely offers the option of deleting it manually. Furthermore, the company also anonymises information (such as advertising data) in server logs by deleting part of the IP address and cookie information after 9 and 18 months respectively.
How can I delete my data or prevent data storage?
With the automatic deletion function for location and activity data introduced in 2019, information on location determination and web/app activity – depending on your decision – is stored for either 3 or 18 months and then deleted. In addition, this data can also be manually deleted from the history at any time via the Google account. If you want to prevent your location from being recorded completely, you must pause the “Web & App Activity” section in your Google account. Click “Data & privacy” and then the option “Activity controls”. Here you can switch the activities on or off.
In your browser you can also deactivate, delete or manage individual cookies. Depending on which browser you use, this always works slightly differently. In the section “Cookies” you will find the corresponding links to the instructions for the most popular browsers.
If you generally do not want cookies, you can set up your browser so that it always informs you when a cookie is to be set. This way you can decide for each individual cookie whether to allow it or not.
Legal basis
If you have consented to the use of Google Maps, the legal basis for the corresponding data processing is this consent. According to Art. 6(1)(a) GDPR (consent) , this consent constitutes the legal basis for the processing of personal data as may occur when it is collected by Google Maps.
We also have a legitimate interest in using Google Maps to optimise our online service. The corresponding legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use Google Maps if you have given your consent.
Google also processes your data in the USA, among other places. Google is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data of EU citizens to the USA. You can find more information on this at https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
In addition, Google uses so-called standard contractual clauses (= Art. 46(2) and (3) GDPR). Standard contractual clauses (SCC) are templates provided by the EU Commission and are intended to ensure that your data also complies with European data protection standards when it is transferred to and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the standard contractual clauses, Google undertakes to comply with the European level of data protection when processing your relevant data, even if the data is stored, processed and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding standard contractual clauses here, among other places: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de
You can find the Google Ads Data Processing Terms, which refer to the standard contractual clauses, at https://business.safety.google/intl/de/adsprocessorterms/.
If you want to learn more about data processing by Google, we recommend the company's own privacy policy at https://policies.google.com/privacy?hl=de.
Content Search Providers Introduction
|
Content Search Providers Privacy Policy Summary
👥 Data subjects: visitors to the website 🤝 Purpose: improving the user experience 📓 Data processed: which data is processed depends heavily on the services used. Usually it is IP address, search interests and/or technical data. You can find more details on this from the respective tools used. 📅 Storage period: depends on the tools used ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is a content search provider?
By now we have published a great deal of content on our website. And of course we do not want it to simply be forgotten just because it is not found. That is why we use a content search provider on our website. You certainly know large search engines like Google. A content search provider is basically also a search engine, which, unlike Google, does not search the entire web for content but only the website you are on. Via a text field you can enter terms that match the content you are looking for, and the search program finds the desired posts for you. If you use the integrated search function, personal data of yours may also be processed.
Why do we use a content search provider?
If you look around our website, you will quickly notice how much useful content we have already published over the years. There are real treasures among it, and we want you to find them quickly without much clicking around. With a content search function directly in our website, you can find the content you are looking for quickly and easily using keywords that match the topic you are looking for. This feature is really practical, and we also see it as our job to make your life on our website as pleasant and helpful as possible. That is why we decided to integrate a content search program into our website.
What data is processed?
When you use the search function on our website, the integrated content search provider (such as Algolia Places or Giphy) may automatically receive and store data from you. This includes technical data about your browser and data such as your IP address, device ID and the search terms entered. Please note that IP addresses are personal data. The providers' privacy policies state that this information is collected and stored to increase security and improve their own services. The automatically collected usage data, which does not include personal data and is processed in anonymised form, may also be used for analysis purposes. Some providers also pass on this anonymised data to third parties. To find out more about this, we recommend that you read the specific privacy policies of the individual providers carefully. In order for the services to work properly, cookies are usually also set in your browser. You can find out more about cookies in our general section “Cookies”. Whether and which cookies the individual search tools use can be found – if available – below or in the corresponding privacy policies of the integrated tools.
How long and where is the data stored?
In principle, each content search provider processes different data. It is therefore not possible to go into the data processing of the individual tools in detail in this general section. Usually, however, the services only store personal data for as long as is necessary for the tools to function smoothly. Some services (such as Giphy) also retain personal data for longer if this is required due to legal obligations. Most providers also retain data in depersonalised form for longer. Content search providers may also use cookies to store various data. You can find out more about this in our general section on cookies. If you want to know something about the specific cookies that a search provider uses, we recommend the privacy policy of the providers we use. There you will usually find an example list of the cookies used.
Right to object
Always be aware: if you do not want it, no personal data of yours may be processed. You always have the right to access your personal data and to object to its use. You can also withdraw your consent at any time via the cookie consent tool or other opt-out options. You can also very easily manage, delete or deactivate cookies used via your browser yourself. If you delete cookies, a few functions of the tool may no longer work. So please do not be surprised. How you manage cookies in your browser also depends on the browser you use. In the section “Cookies” you will also find links to the instructions for the most important browsers.
Legal basis
If you have consented to the use of a content search provider, the legal basis for the corresponding data processing is this consent. According to Art. 6(1)(a) GDPR (consent), this consent constitutes the legal basis for the processing of personal data as may occur when it is collected by a content search provider.
We also have a legitimate interest in using a content search provider to optimise our service on our website. The corresponding legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). However, we only ever use a content search provider if you have given your consent. We definitely want to state this again at this point.
Information on specific content search providers can be found – if available – in the following sections.
Google Custom Search Privacy Policy
|
Google Custom Search Privacy Policy Summary
👥 Data subjects: visitors to the website 🤝 Purpose: optimising our service 📓 Data processed: data such as IP address and search terms entered are stored by Google You can find more details on this further down in this privacy policy. 📅 Storage period: the storage period varies depending on the data stored ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What is Google Custom Search?
We have integrated the Google plug-in for custom search on our website. Google is the largest and best-known search engine in the world and is operated by the US company Google Inc. For the European area, the company Google Ireland Limited (Gordon House, Barrow Street Dublin 4, Ireland) is responsible. Through Google Custom Search, data of yours may be transferred to Google. In this privacy policy we inform you why we use this plug-in, which data is processed and how you can manage or prevent this data transfer.
The Google Custom Search plug-in is a Google search bar directly on our website. The search takes place as on www.google.com , only the search results focus on our content and products or on a restricted search scope.
Why do we use Google Custom Search on our website?
A website with a lot of interesting content often becomes so large that you may lose track. Over time we too have accumulated a lot of valuable material, and as part of our service we want you to find our content as quickly and easily as possible. With Google Custom Search, finding interesting content becomes child's play. The built-in Google plug-in improves the overall quality of our website and makes searching easier for you.
What data is stored by Google Custom Search?
Google Custom Search only transfers data from you to Google if you actively use the Google search built into our website. This means that only when you enter a search term in the search bar and then confirm this term (e.g. click “Enter”) is your IP address sent to Google, stored and processed there in addition to the search term. Based on the cookies set (such as 1P_JAR), it can be assumed that Google also receives data on website usage. If, during your visit to our website, you search for content via the built-in Google search function and are logged in to your Google account at the same time, Google can also assign the collected data to your Google account. As the website operator, we have no influence on what Google does with the collected data or how Google processes the data.
The following cookies are set in your browser if you use Google Custom Search and are not logged in with a Google account:
Name: 1P_JAR
Value: 2020-01-27-13113097992-5
Purpose: This cookie collects statistics on website usage and measures conversions. A conversion occurs, for example, when a user becomes a buyer. The cookie is also used to display relevant advertisements to users.
Expiry date: after one month
Name: CONSENT
Value: WP.282f52113097992-9
Purpose: The cookie stores the status of a user's consent to the use of various Google services. CONSENT also serves security purposes, to verify users and protect user data from unauthorised attacks.
Expiry date: after 18 years
Name: NID
Value: 196=pwIo3B5fHr-8
Purpose: NID is used by Google to tailor advertisements to your Google search. With the help of the cookie, Google “remembers” your entered search queries or your previous interaction with ads. This way you always receive tailor-made advertisements.
Expiry date: after 6 months
Note: This list cannot claim to be complete, as Google repeatedly changes its choice of cookies.
How long and where is the data stored?
The Google servers are distributed all over the world. Since Google is an American company, most data is stored on American servers. At https://www.google.com/about/datacenters/locations/?hl=de you can see exactly where the Google servers are located.
Your data is distributed across different physical data carriers. This makes the data quicker to retrieve and better protected against possible manipulation. Google also has appropriate emergency programmes for your data. If, for example, there are internal technical problems at Google and servers therefore no longer work, the risk of a service interruption and data loss still remains low.
Google stores data for different lengths of time depending on the type of data. You can delete some data yourself, other data is automatically deleted or anonymised by Google. However, there is also data that Google stores for longer if this is necessary for legal or business reasons.
How can I delete my data or prevent data storage?
Under the data protection law of the European Union, you have the right to obtain information about your data and to update, delete or restrict it. There is some data that you can delete at any time. If you have a Google account, you can delete data on your web activity there or specify that it should be deleted after a certain time.
In your browser you also have the option of deactivating, deleting or managing cookies according to your wishes and preferences. In the section “Cookies” you will find the corresponding links to the instructions for the most popular browsers.
Legal basis
If you have consented to the use of Google Custom Search, the legal basis for the corresponding data processing is this consent. According to Art. 6(1)(a) GDPR (consent) , this consent constitutes the legal basis for the processing of personal data as may occur when it is collected by Google Custom Search.
We also have a legitimate interest in using Google Custom Search to optimise our online service. The corresponding legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use Google Custom Search if you have given your consent.
Google also processes your data in the USA, among other places. Google is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data of EU citizens to the USA. You can find more information on this at https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
In addition, Google uses so-called standard contractual clauses (= Art. 46(2) and (3) GDPR). Standard contractual clauses (SCC) are templates provided by the EU Commission and are intended to ensure that your data also complies with European data protection standards when it is transferred to and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the standard contractual clauses, Google undertakes to comply with the European level of data protection when processing your relevant data, even if the data is stored, processed and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding standard contractual clauses here, among other places: https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de
You can find the Google Ads Data Processing Terms, which refer to the standard contractual clauses, at https://business.safety.google/intl/de/adsprocessorterms/
We hope we have been able to give you the most important information about data processing by Google. If you want to learn more about it, we recommend Google's comprehensive privacy policy at https://policies.google.com/privacy?hl=de.
Other Services Introduction
|
Other Services Privacy Policy Summary
👥 Data subjects: visitors to the website 🤝 Purpose: improving the user experience 📓 Data processed: which data is processed depends heavily on the services used. Usually it is IP address and/or technical data. You can find more details on this from the respective tools used. 📅 Storage period: depends on the tools used ⚖️ Legal bases: Art. 6(1)(a) GDPR (consent), Art. 6(1)(f) GDPR (legitimate interests) |
What falls under “Other”?
The category “Other” includes those services that do not fit into any of the categories mentioned above. These are usually various plugins and integrated elements that improve our website. As a rule, these functions are obtained from third-party providers and integrated into our website. Examples include web search services such as Algolia Place, Giphy, Programmable Search Engine or online services for weather data such as OpenWeather.
Why do we use other third-party providers?
With our website we want to offer you the best web offering in our industry. For a long time now, a website has not merely been a business card for companies. Rather, it is a place that should help you find what you are looking for. In order to make our website ever more interesting and helpful for you, we use various services from third-party providers.
What data is processed?
Whenever elements are integrated into our website, your IP address is transmitted to the respective provider, stored and processed there. This is necessary because otherwise the content would not be sent to your browser and consequently would not be displayed properly. It may also happen that service providers also use pixel tags or web beacons. These are small graphics on websites that record a log file and can also create analyses of this file. With the information obtained, the providers can improve their own marketing measures. In addition to pixel tags, such information (such as which button you click or when you call up which page) can also be stored in cookies. In addition to analysis data on your web behaviour, technical information such as your browser type or operating system may also be stored there. Some providers can also link the data obtained with other internal services or with third-party providers. Each provider handles your data differently. We therefore recommend that you read the privacy policies of the respective services carefully. In principle, we endeavour to use only services that handle the topic of data protection very carefully.
Duration of data processing
We will inform you about the duration of data processing below, provided we have further information on this. In general, we only process personal data for as long as is absolutely necessary to provide our services and products.
Legal basis
If we ask for your consent and you consent to us using the service, this is the legal basis for processing your data (Art. 6(1)(a) GDPR). In addition to consent, we have a legitimate interest in analysing the behaviour of website visitors and thus improving our offer technically and economically. The legal basis for this is Art. 6(1)(f) GDPR (legitimate interests). Nevertheless, we only use the tools if you have given your consent.
Information on the specific tools can be found – if available – in the following sections.
Explanation of Terms Used
We always endeavour to write our privacy policy as clearly and comprehensibly as possible. However, this is not always easy, especially with technical and legal topics. It often makes sense to use legal terms (such as personal data) or certain technical expressions (such as cookies, IP address). However, we do not want to use them without explanation. Below you will now find an alphabetical list of important terms used that we may not yet have covered sufficiently in the privacy policy so far. If these terms have been taken from the GDPR and are definitions, we will also quote the GDPR texts here and, where appropriate, add our own explanations.
Supervisory authority
Definition according to Article 4 GDPR
For the purposes of this Regulation:
“supervisory authority” means an independent public authority which is established by a Member State pursuant to Article 51;
Explanation: “Supervisory authorities” are always independent state bodies that are also authorised to issue instructions in certain cases. They serve to carry out so-called state supervision and are located in ministries, special departments or other authorities. For data protection in Austria there is an Austrian Data Protection Authority (Datenschutzbehörde), while in Germany there is a separate data protection authority for each federal state.
Processor
Definition according to Article 4 GDPR
For the purposes of this Regulation:
“processor” means a natural or legal person, public authority, agency or other body which processes personal data on behalf of the controller;
Explanation: As a company and website owner, we are responsible for all data that we process from you. In addition to the controllers, there may also be so-called processors. This includes any company or person that processes personal data on our behalf. In addition to service providers such as tax advisers, processors can therefore also be hosting or cloud providers, payment or newsletter providers or large companies such as Google or Microsoft.
Supervisory authority concerned
Definition according to Article 4 GDPR
For the purposes of this Regulation:
“supervisory authority concerned” means a supervisory authority which is concerned by the processing of personal data because:
a)
the controller or processor is established on the territory of the Member State of that supervisory authority;
b)
data subjects residing in the Member State of that supervisory authority are substantially affected or likely to be substantially affected by the processing; or
c)
a complaint has been lodged with that supervisory authority;
Explanation: In Germany, each federal state has its own supervisory authority for data protection. So if your company headquarters (main establishment) is in Germany, the respective supervisory authority of the federal state is generally your contact. In Austria there is only one supervisory authority for data protection.
Biometric data
Definition according to Article 4 GDPR
For the purposes of this Regulation:
“biometric data” means personal data resulting from specific technical processing relating to the physical, physiological or behavioural characteristics of a natural person, which allow or confirm the unique identification of that natural person, such as facial images or dactyloscopic data;
Explanation: These are biological characteristics described by biometric data, from which personal data can be obtained with the help of technical processes. These include, for example, DNA, fingerprints, the geometry of various body parts, height, but also handwriting or the sound of a voice.
Filing system
Definition according to Article 4 GDPR
For the purposes of this Regulation:
“filing system” means any structured set of personal data which are accessible according to specific criteria, whether centralised, decentralised or dispersed on a functional or geographical basis;
Explanation: Any organised storage of data on a computer's data carrier is referred to as a “filing system”. If, for example, we store your name and email address on a server for our newsletter, this data is in a so-called “filing system”. The most important tasks of a “filing system” include quickly searching for and finding specific data and, of course, storing the data securely.
Information society service
Definition according to Article 4 GDPR
For the purposes of this Regulation:
“information society service” means a service as defined in point (b) of Article 1(1) of Directive (EU) 2015/1535 of the European Parliament and of the Council (19);
Explanation: Basically, the term “information society” refers to a society based on information and communication technologies. Especially as a website visitor, you are familiar with a wide variety of online services, and most online services count as “information society services”. A classic example of this is an online transaction, such as the purchase of goods via the internet.
Third party
Definition according to Article 4 GDPR
For the purposes of this Regulation:
“third party” means a natural or legal person, public authority, agency or body other than the data subject, controller, processor and persons who, under the direct authority of the controller or processor, are authorised to process personal data;
Explanation: Basically, the GDPR only explains here what a “third party” is not. In practice, a “third party” is anyone who is also interested in the personal data but does not belong to the persons, authorities or bodies mentioned above. For example, a parent company can act as a “third party”. In this case, the subsidiary is the controller and the parent company a “third party”. However, this does not mean that the parent company may automatically view, collect or store the personal data of the subsidiary.
Restriction of processing
Definition according to Article 4 GDPR
For the purposes of this Regulation:
“restriction of processing” means the marking of stored personal data with the aim of limiting their processing in the future;
Explanation: It is one of your rights that you can request processors at any time to restrict your personal data for further processing operations. For this purpose, specific personal data such as your name, date of birth or address are marked in such a way that full further processing is no longer possible. For example, you could restrict the processing so that your data may no longer be used for personalised advertising.
Consent
Definition according to Article 4 GDPR
For the purposes of this Regulation:
“consent” of the data subject means any freely given, specific, informed and unambiguous indication of the data subject's wishes by which he or she, by a statement or by a clear affirmative action, signifies agreement to the processing of personal data relating to him or her;
Explanation: On websites, such consent is usually given via a cookie consent tool. You are certainly familiar with this. Whenever you visit a website for the first time, you are usually asked via a banner whether you agree or consent to the data processing. Usually you can also make individual settings and thus decide for yourself which data processing you allow and which you do not. If you do not consent, no personal data of yours may be processed. In principle, consent can of course also be given in writing, i.e. not via a tool.
Recipient
Definition according to Article 4 GDPR
For the purposes of this Regulation:
“recipient” means a natural or legal person, public authority, agency or another body, to which the personal data are disclosed, whether a third party or not. However, public authorities which may receive personal data in the framework of a particular inquiry in accordance with Union or Member State law shall not be regarded as recipients; the processing of those data by those public authorities shall be in compliance with the applicable data protection rules according to the purposes of the processing;
Explanation: Every person and every company that receives personal data is considered a recipient. This means that we and our processors are also so-called recipients. Only authorities with an investigative mandate are not considered recipients.
Genetic data
Definition according to Article 4 GDPR
For the purposes of this Regulation:
“genetic data” means personal data relating to the inherited or acquired genetic characteristics of a natural person which give unique information about the physiology or the health of that natural person and which result, in particular, from an analysis of a biological sample from the natural person in question;
Explanation: With a certain amount of effort, people can be identified via genetic data. That is why genetic data also falls into the category of personal data. Genetic data is obtained, for example, from blood or saliva samples.
Data concerning health
Definition according to Article 4 GDPR
For the purposes of this Regulation:
“data concerning health” means personal data related to the physical or mental health of a natural person, including the provision of health care services, which reveal information about his or her health status;
Explanation: Health data therefore includes all stored information that concerns your own health. Often this is data that is also recorded in a patient file. This includes, for example, which medication you take, X-ray images, your entire medical history or usually also your vaccination status.
Cross-border processing
Definition according to Article 4 GDPR
For the purposes of this Regulation:
“cross-border processing” means either
a)
processing of personal data which takes place in the context of the activities of establishments in more than one Member State of a controller or processor in the Union where the controller or processor is established in more than one Member State; or
b)
processing of personal data which takes place in the context of the activities of a single establishment of a controller or processor in the Union but which substantially affects or is likely to substantially affect data subjects in more than one Member State;
Explanation: If, for example, a company or other organisation has establishments in Spain and Croatia and personal data is processed in connection with the activities of the establishments, this is “cross-border processing” of personal data. Even if the data is only processed in one country (as in this example in Spain) but the effects for the data subject are also noticeable in another country, this is also referred to as “cross-border processing”.
Main establishment
Definition according to Article 4 GDPR
For the purposes of this Regulation:
“main establishment”
a)
means as regards a controller with establishments in more than one Member State, the place of its central administration in the Union, unless the decisions on the purposes and means of the processing of personal data are taken in another establishment of the controller in the Union and the latter establishment has the power to have such decisions implemented, in which case the establishment having taken such decisions is to be considered to be the main establishment;
b)
as regards a processor with establishments in more than one Member State, the place of its central administration in the Union, or, if the processor has no central administration in the Union, the establishment of the processor in the Union where the main processing activities in the context of the activities of an establishment of the processor take place to the extent that the processor is subject to specific obligations under this Regulation;
Explanation: The company Google, for example, is an American company that also processes data in the USA, but its European main establishment is in Ireland (Google Ireland Limited, Gordon House, Barrow Street Dublin 4, Ireland). Legally, Google Ireland Limited is therefore an independent company and responsible for all Google products offered in the European Economic Area. In contrast to a main establishment, there are also branch offices, but these do not function as legally independent establishments and must therefore also be distinguished from subsidiaries. A main establishment is therefore always the place where a company (trading company) has its centre of operations.
International organisation
Definition according to Article 4 GDPR
For the purposes of this Regulation:
“international organisation” means an organisation and its subordinate bodies governed by public international law, or any other body which is set up by, or on the basis of, an agreement between two or more countries.
Explanation: The best-known examples of international organisations are probably the European Union or the United Nations. The GDPR distinguishes between third countries and international organisations in connection with data transfers. Within the EU, the transfer of personal data is not a problem because all EU countries are bound by the requirements of the GDPR. In contrast, data transfers to third countries or international organisations are subject to certain conditions.
Relevant and reasoned objection
Definition according to Article 4 GDPR
For the purposes of this Regulation:
“relevant and reasoned objection” means an objection to a draft decision as to whether there is an infringement of this Regulation, or whether envisaged action in relation to the controller or processor complies with this Regulation, which clearly demonstrates the significance of the risks posed by the draft decision as regards the fundamental rights and freedoms of data subjects and, where applicable, the free flow of personal data within the Union;
Explanation: If certain measures that we as the controller or our processors take are not in line with the GDPR, you can raise a so-called “relevant and reasoned objection”. In doing so, you must explain the significance of the risks with regard to your fundamental rights and freedoms and possibly the free flow of your personal data in the EU.
Personal data
Definition according to Article 4 GDPR
For the purposes of this Regulation:
“personal data” means any information relating to an identified or identifiable natural person (“data subject”); an identifiable natural person is one who can be identified, directly or indirectly, in particular by reference to an identifier such as a name, an identification number, location data, an online identifier or to one or more factors specific to the physical, physiological, genetic, mental, economic, cultural or social identity of that natural person;
Explanation: Personal data is therefore all data that can identify you as a person. This is usually data such as:
- Name
- Address
- Email address
- Postal address
- Phone number
- Date of birth
- Identification numbers such as social security number, tax identification number, identity card number or student ID number
- Bank details such as account number, credit information, account balances and much more.
According to the European Court of Justice (ECJ), your IP address also counts as personal data. IT experts can use your IP address to determine at least the approximate location of your device and subsequently you as the connection owner. Therefore, storing an IP address also requires a legal basis within the meaning of the GDPR. There are also so-called “special categories” of personal data, which are particularly worthy of protection. These include:
- racial and ethnic origin
- political opinions
- religious or philosophical beliefs
- trade union membership
- genetic data, such as data taken from blood or saliva samples
- biometric data (this is information on mental, physical or behavioural characteristics that can identify a person).
Data concerning health - data concerning sexual orientation or sex life
Profiling
Definition according to Article 4 GDPR
For the purposes of this Regulation:
“profiling” means any form of automated processing of personal data consisting of the use of personal data to evaluate certain personal aspects relating to a natural person, in particular to analyse or predict aspects concerning that natural person's performance at work, economic situation, health, personal preferences, interests, reliability, behaviour, location or movements;
Explanation: In profiling, various pieces of information about a person are compiled in order to learn more about that person. On the web, profiling is often used for advertising purposes or for credit checks. Web or advertising analysis programs, for example, collect data about your behaviour and interests on a website. This results in a special user profile that can be used to target advertising at a specific audience.
Pseudonymisation
Definition according to Article 4 GDPR
For the purposes of this Regulation:
“pseudonymisation” means the processing of personal data in such a manner that the personal data can no longer be attributed to a specific data subject without the use of additional information, provided that such additional information is kept separately and is subject to technical and organisational measures to ensure that the personal data are not attributed to an identified or identifiable natural person;
Explanation: Our privacy policy often refers to pseudonymised data. Pseudonymised data means that you can no longer be identified as a person unless other information is added. However, you should not confuse pseudonymisation with anonymisation. With anonymisation, any personal reference is removed, so that it can really only be reconstructed with disproportionately great technical effort.
Enterprise
Definition according to Article 4 GDPR
For the purposes of this Regulation:
“enterprise” means a natural or legal person engaged in an economic activity, irrespective of its legal form, including partnerships or associations regularly engaged in an economic activity;
Explanation: We, for example, are an enterprise and also carry out an economic activity via our website by offering and selling services and/or products. For every enterprise, the formal characteristic is its legal form, such as a GmbH (limited liability company) or an AG (public limited company).
Group of undertakings
Definition according to Article 4 GDPR
For the purposes of this Regulation:
“group of undertakings” means a controlling undertaking and its controlled undertakings;
Explanation: So we speak of a “group of undertakings” when several companies join together and are legally and financially connected with each other, but there is still a central company at the top. For example, Instagram, WhatsApp, Oculus VR and Facebook are largely independent companies, but are all subject to the parent company Meta Platforms, Inc.
Controller
Definition according to Article 4 GDPR
For the purposes of this Regulation:
“controller” means the natural or legal person, public authority, agency or other body which, alone or jointly with others, determines the purposes and means of the processing of personal data; where the purposes and means of such processing are determined by Union or Member State law, the controller or the specific criteria for its nomination may be provided for by Union or Member State law;
Explanation: In our case, we are responsible for the processing of your personal data and are therefore the “controller”. If we pass on collected data to other service providers for processing, they are “processors”. For this, a “data processing agreement (DPA)” must be signed.
Processing
Definition according to Article 4 GDPR
For the purposes of this Regulation:
“processing” means any operation or set of operations which is performed on personal data or on sets of personal data, whether or not by automated means, such as collection, recording, organisation, structuring, storage, adaptation or alteration, retrieval, consultation, use, disclosure by transmission, dissemination or otherwise making available, alignment or combination, restriction, erasure or destruction;
Note: When we speak of processing in our privacy policy, we mean any kind of data processing. As mentioned above in the original GDPR definition, this includes not only the collection but also the storage and processing of data.
Binding corporate rules
Definition according to Article 4 GDPR
For the purposes of this Regulation:
“binding corporate rules” means personal data protection policies which are adhered to by a controller or processor established on the territory of a Member State for transfers or a set of transfers of personal data to a controller or processor in one or more third countries within a group of undertakings, or group of enterprises engaged in a joint economic activity;
Explanation: You may have heard or read the term “binding corporate rules” before. This is the term that usually appears when it comes to internal data protection rules. Such an internal rule, by which a company commits itself, so to speak, to comply with data protection regulations, is particularly advisable for companies (such as Google) that process data in third countries. This rule governs the handling of personal data that is transferred to and processed in third countries.
Personal data breach
Definition according to Article 4 GDPR
For the purposes of this Regulation:
“personal data breach” means a breach of security leading to the accidental or unlawful destruction, loss, alteration, unauthorised disclosure of, or access to, personal data transmitted, stored or otherwise processed;
Explanation: For example, a “personal data breach” can occur in the event of a data leak, i.e. a technical problem or a cyber attack. If the breach results in a risk to the rights and freedoms of natural persons, the controller must report the incident to the competent supervisory authority immediately. In addition, the data subjects must also be informed if the breach poses a high risk to the rights and freedoms of natural persons.
Representative
Definition according to Article 4 GDPR
For the purposes of this Regulation:
“representative” means a natural or legal person established in the Union who, designated by the controller or processor in writing pursuant to Article 27, represents the controller or processor with regard to their respective obligations under this Regulation;
Explanation: A “representative” can therefore be any person who has been appointed in writing by us (controller) or one of our service providers (processor). Companies outside the EU that process data of EU citizens must name a representative within the EU. If, for example, a web analytics provider has its main establishment in the USA, it must appoint a “representative” within the European Union to represent its obligations with regard to data processing.
Closing Remarks
Congratulations! If you are reading these lines, you have really “fought” your way through our entire privacy policy or at least scrolled this far. As you can see from the scope of our privacy policy, we take the protection of your personal data anything but lightly.
It is important to us to inform you to the best of our knowledge and belief about the processing of personal data. In doing so, we want to tell you not only which data is processed but also explain the reasons for using various software programs. Privacy policies usually sound very technical and legal. However, since most of you are not web developers or lawyers, we also wanted to take a different approach linguistically and explain the facts in simple and clear language. Of course, this is not always possible due to the subject matter. That is why the most important terms are explained in more detail at the end of the privacy policy.
If you have any questions about data protection on our website, please do not hesitate to contact us or the responsible body. We wish you a pleasant time and hope to welcome you back to our website soon.
All texts are protected by copyright.
Source: Privacy Policy created with the Data Protection Generator for Austria by AdSimple